
Beehaw
  • Communities
  • Create Post
  • search
    Search
  • Login
  • Sign Up
mr_MADAFAKA ( mr_MADAFAKA@lemmy.ml )  to Linux@lemmy.ml · 3 years ago

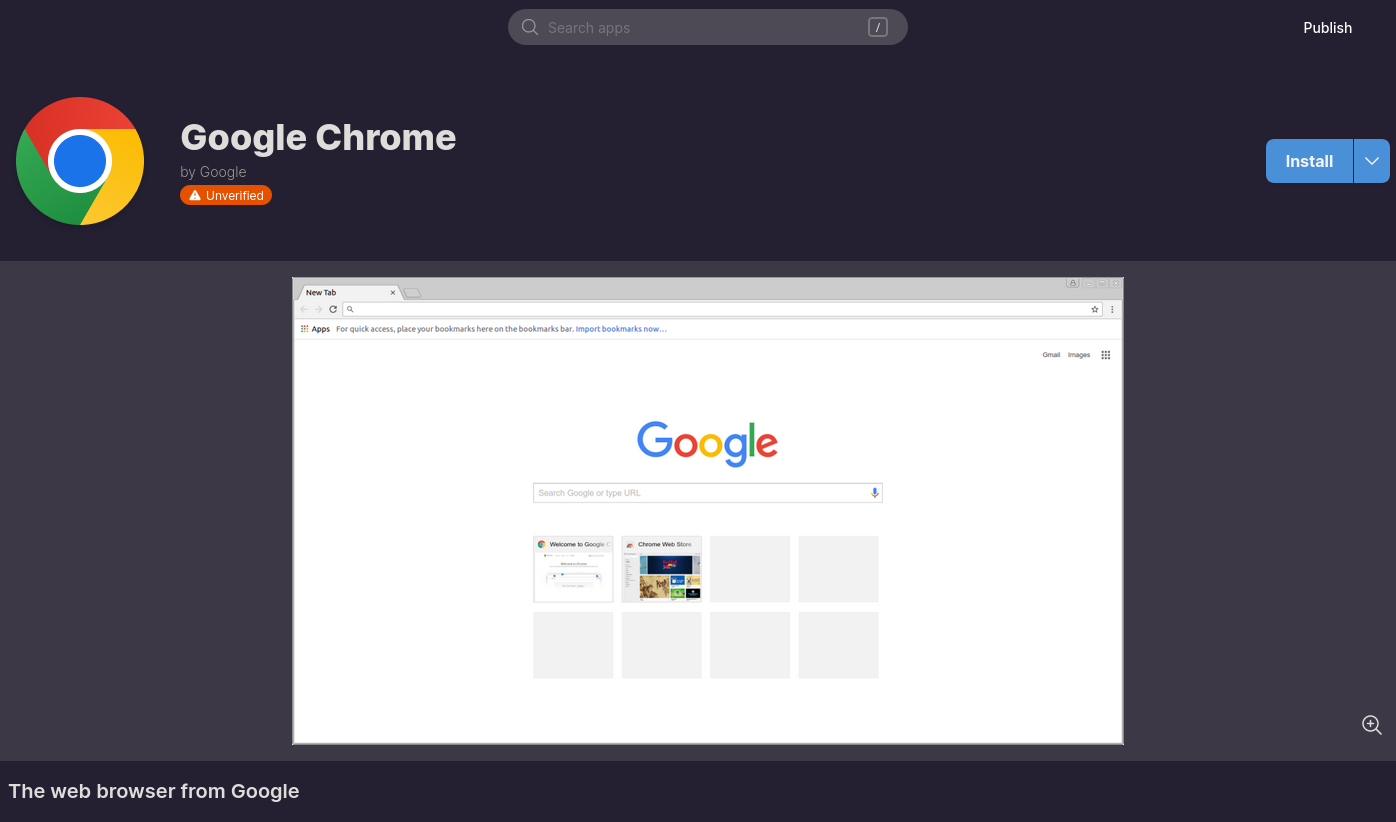
Flathub now marks unverified apps

lemmy.ml

message-square
41
link
fedilink
278

Flathub now marks unverified apps

lemmy.ml

mr_MADAFAKA ( mr_MADAFAKA@lemmy.ml )  to Linux@lemmy.ml · 3 years ago
message-square
41
link
fedilink
alert-triangle
You must log in or # to comment.
  • tanja ( tanja@lemmy.blahaj.zone ) 
    link
    fedilink
    arrow-up
    110
    ·
    3 years ago

    Nice

    Good to see one of the two big packaging hubs do something against malware

    • thingsiplay ( thingsiplay@beehaw.org ) 
      link
      fedilink
      arrow-up
      14
      ·
      3 years ago

      Next step, display the “potential unsafe”-badge next to verified or unverified, that can be found on the same page. In example https://flathub.org/apps/io.github.shiiion.primehack is marked as verified, but if you scroll down you can see the application has full system and data access and is marked as potential unsafe.

    • Pantherina ( Pantherina@feddit.de ) 
      link
      fedilink
      arrow-up
      12
      ·
      3 years ago

      Verification doesnt help at all if the source is not trusted. All this says is “upstream developers maintain this package”. Unofficial packages can be safe too, like VLC.

      • dsemy ( dsemy@lemm.ee ) 
        link
        fedilink
        English
        arrow-up
        40
        ·
        edit-2
        2 years ago

        deleted by creator

        • Pantherina ( Pantherina@feddit.de ) 
          link
          fedilink
          arrow-up
          9
          ·
          3 years ago

          If you create malware and publish it on flathub, you are the upstream dev. But for sure it helps against duplicate scams.

          • dsemy ( dsemy@lemm.ee ) 
            link
            fedilink
            English
            arrow-up
            16
            ·
            edit-2
            2 years ago

            deleted by creator

            • Pantherina ( Pantherina@feddit.de ) 
              link
              fedilink
              arrow-up
              3
              ·
              3 years ago

              Nice!

              Add flathub with --subset=verified and get apps you really need from their .flatpakref files

        • Pantherina ( Pantherina@feddit.de ) 
          link
          fedilink
          arrow-up
          8
          ·
          3 years ago

          Flathub is doing more and more, but stuff like hiding --subset=verified is very bad.

          They simply need to gain critical mass until they can force changes like portals etc.

        • pmk ( pmk@lemmy.sdf.org ) 
          link
          fedilink
          arrow-up
          2
          ·
          3 years ago

          Fedora has their own flatpak repo built from their own rpms and their own runtime. Flathub has more flatpaks though.

        • thingsiplay ( thingsiplay@beehaw.org ) 
          link
          fedilink
          arrow-up
          1
          ·
          3 years ago

          This unverified badge does not prevent from malware being downloaded. This is a false statement! An upstream developer can have malicious intention and be verified as the upstream developer. This unverified badge only helps identifying its not a modified version by someone else and is guaranteed to be from the original developer. It does not prevent anyone from downloading and installing unverified apps. If that was the goal, then why having unverified apps in the first place on the store? Yes, because its useful. Therefore people will download unverified apps or just blindly trust verified apps.

          At the moment his is enough. But if the Flathub store grows, this can be an issue. Look at the Android and ios app stores; there are plenty of apps from original developers with malicious intentions.

          • dsemy ( dsemy@lemm.ee ) 
            link
            fedilink
            English
            arrow-up
            2
            ·
            edit-2
            2 years ago

            deleted by creator

            • thingsiplay ( thingsiplay@beehaw.org ) 
              link
              fedilink
              arrow-up
              1
              ·
              3 years ago

              That’s my point, it does not “help” preventing from malware from being downloaded.

              • dsemy ( dsemy@lemm.ee ) 
                link
                fedilink
                English
                arrow-up
                8
                ·
                edit-2
                2 years ago

                deleted by creator

    • Cwilliams ( Cwilliams@beehaw.org ) 
      link
      fedilink
      arrow-up
      10
      ·
      3 years ago

      cough cough snap cough

      • Montagge ( Montagge@lemmy.zip ) 
        link
        fedilink
        arrow-up
        5
        ·
        3 years ago

        Snap already marks unverified apps

        • ThermoToaster ( ThermoToaster@exng.meme ) 
          link
          fedilink
          arrow-up
          1
          ·
          3 years ago

          Yet Ubuntu still recommends installing anything from the terminal if a command was found in a rando unverified snap.

    • JakobDev ( JakobDev@feddit.de ) 
      link
      fedilink
      arrow-up
      3
      ·
      3 years ago

      How does that Help against Malware?

      • unionagainstdhmo ( unionagainstdhmo@aussie.zone ) 
        link
        fedilink
        English
        arrow-up
        8
        ·
        edit-2
        2 years ago

        deleted by creator

    • delirious_owl ( delirious_owl@discuss.online ) 
      link
      fedilink
      arrow-up
      1
      ·
      3 years ago

      Apt has done this forever

  • Captain Beyond ( beyond@linkage.ds8.zone ) 
    link
    fedilink
    arrow-up
    14
    ·
    3 years ago

    Traditional GNU/Linux distributions (as well as F-Droid) are not “app stores” even though they are superficially similar. Traditional distributions are maintained and curated by the community, and serve the interests of users first and software developers second, whereas an “app store” has minimal curation and serves the needs of software developers first and users second.

    I point this out because there’s an annoying meme that traditional distributions are obsoleted by the “app store” model. I don’t think that’s the case. “Verification” is essential for an app store but pointless for a distribution.

  • pewgar_kbin ( pewgar_kbin@fedia.io ) 
    link
    fedilink
    arrow-up
    10
    ·
    3 years ago

    great, when appimage hub begin doing this

    • thingsiplay ( thingsiplay@beehaw.org ) 
      link
      fedilink
      arrow-up
      10
      ·
      3 years ago

      I still don’t understand why a central repository for AppImages exist. The moment you are using a repository (and possibly version management), the format looses its reason to exist.

      • GnomeComedy ( GnomeComedy@beehaw.org ) 
        link
        fedilink
        arrow-up
        10
        ·
        3 years ago

        I don’t see how that’s true. The main point of AppImage is it ‘just works’ on any distro. If you have one primary place to distribute them to any distro - it’s still meeting AppImage’s vision.

        • thingsiplay ( thingsiplay@beehaw.org ) 
          link
          fedilink
          arrow-up
          8
          ·
          3 years ago

          To be fair, after some thinking I think you are right and I was a bit in a tunnel vision logic. My previous statement looks a bit foolish now.

      • Pantherina ( Pantherina@feddit.de ) 
        link
        fedilink
        arrow-up
        6
        ·
        3 years ago

        No. Appimages are selfcontained and thus useful for archiving software or carrying it around in random ways. Flatpak could do this too but not as easy.

        Still, don’t use Appimages

        • thingsiplay ( thingsiplay@beehaw.org ) 
          link
          fedilink
          arrow-up
          1
          ·
          3 years ago

          I personally use a few AppImages, but want replace them with Flatpaks. Flatpaks have their own issues, and because I did not want to troubleshoot in case I encounter another issue, just carry on using AppImages for these selected applications. Also I was not able to archive Flatpak easily, its very complicated with keys and not. Compared to it, I just have the AppImages included in my regular backup process with regular files.

          My point was not if AppImages are useful (they clearly are and I use them), but was talking bout repositories. However after some other replies I thought about it and indeed such a repository makes sense even for AppImages. I personally just don’t have to use them.

          • Pantherina ( Pantherina@feddit.de ) 
            link
            fedilink
            arrow-up
            1
            ·
            3 years ago

            Even with such a repo they are highly insecure by design.

            • thingsiplay ( thingsiplay@beehaw.org ) 
              link
              fedilink
              arrow-up
              1
              ·
              3 years ago

              Not really. AppImages are as much secure as any other executable you run on your system. If you download it from a trusted source, like you download trusted Flatpaks or your systems repository, then they are not worse. If you say AppImages are highly insecure, because you run executable code, then you have to take that logic to any other executable format. The problem is not the format itself that makes it insecure, it’s the source.

              • Pantherina ( Pantherina@feddit.de ) 
                link
                fedilink
                arrow-up
                2
                ·
                3 years ago

                No they arent. Please read the linked post.

                • thingsiplay ( thingsiplay@beehaw.org ) 
                  link
                  fedilink
                  arrow-up
                  2
                  ·
                  3 years ago

                  I read that page and there is nonsense included too. Just because I read that page does not make it correct. If you think that AppImages insecure, then you did not understand my point that its not the format thats insecure, but the source where you get the files. Every packaging system is insecure if you get it from bad source.

                  That’s not even a question. AppImages are fine and not insecure if you download it from a secure place you trust (like your system packages, you trust your distro maintainer fully). Would you trust every distribution maintainer on every distribution? Let’s say a Chinese Linux distribution, that maintains Flatpaks and native packages. Let’s say they are flaky. See? It’s the source you don’t trust, not the file format or packaging system.

                  Read my replies (just like you said I should read the linked post). And understand the issues.

  • delirious_owl ( delirious_owl@discuss.online ) 
    link
    fedilink
    arrow-up
    9
    ·
    3 years ago

    So all of them?

    Would be nice if FlatHub actually supported cryptographic verification of apps…

  • JackGreenEarth ( JackGreenEarth@lemm.ee ) 
    link
    fedilink
    English
    arrow-up
    4
    ·
    3 years ago

    What app is that GUI from?

    • Spectranox ( UmbraTemporis@lemmy.dbzer0.com ) 
      link
      fedilink
      English
      arrow-up
      25
      ·
      3 years ago

      This screenshot is from the Flathub website. The only good GUI for Flatpaks…

      • simple ( simple@lemm.ee ) 
        link
        fedilink
        English
        arrow-up
        17
        ·
        3 years ago

        The only good GUI for Flatpaks…

        Ain’t that the truth. I don’t know why KDE Discover is so sluggish when it comes to Flatpak, it takes me like 10+ seconds to load the landing page and see the popular apps.

        • Something Burger 🍔 ( SomethingBurger@jlai.lu ) 
          link
          fedilink
          arrow-up
          7
          ·
          3 years ago

          And several minutes to update a 10MB app…

          • Vilian ( Vilian@lemmy.ca ) 
            link
            fedilink
            arrow-up
            5
            ·
            3 years ago

            what? there’s something wrong with your internet

            • Something Burger 🍔 ( SomethingBurger@jlai.lu ) 
              link
              fedilink
              arrow-up
              4
              ·
              edit-2
              3 years ago

              Nah, it’s Discover that’s shit. Flatpak’s CLI works fine.

        • Cwilliams ( Cwilliams@beehaw.org ) 
          link
          fedilink
          arrow-up
          4
          ·
          3 years ago

          Seriously why does Gnome software feel so much faster!

          • Spectranox ( UmbraTemporis@lemmy.dbzer0.com ) 
            link
            fedilink
            English
            arrow-up
            4
            ·
            3 years ago

            First time I’ve heard someone call Gnome Software fast. In my experience that app feels like it’s on it’s last legs; the Flatpak CLI is far better than any desktop GUI.

            • Chewy ( Chewy7324@discuss.tchncs.de ) 
              link
              fedilink
              arrow-up
              4
              ·
              edit-2
              3 years ago

              Gnome Software has received numerous updates over the last few years which make it considerable faster. Searching and viewing apps is now fast enough to be usable, compared to it taking many seconds to minutes for basic tasks.

              I’ve stopped removing Software on every system, altough I’m not usually using it. I’ve not tested it, but I feel like Discover is now slower than Software.

              • Pantherina ( Pantherina@feddit.de ) 
                link
                fedilink
                arrow-up
                3
                ·
                3 years ago

                COSMIC Appstore ;D

            • Cwilliams ( Cwilliams@beehaw.org ) 
              link
              fedilink
              arrow-up
              1
              ·
              3 years ago

              I’m not saying it’s fast; I’m saying that it’s faster than KDE Discover

          • Russ ( russjr08@bitforged.space ) 
            link
            fedilink
            English
            arrow-up
            1
            ·
            3 years ago

            My main issue with Gnome Software is if I queue something to install, and go back to browse for more apps, once something is done installing it “refreshed” and I lose the spot I was at. Makes me feel I can only install one thing at a time.

      • Pantherina ( Pantherina@feddit.de ) 
        link
        fedilink
        arrow-up
        3
        ·
        3 years ago

        Gnome Software is pretty similar. KDE Discover way worse.

  • Yearly1845 ( Yearly1845@reddthat.com ) 
    link
    fedilink
    arrow-up
    1
    ·
    edit-2
    2 years ago

    deleted by creator

Linux@lemmy.ml

linux@lemmy.ml

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !linux@lemmy.ml

From Wikipedia, the free encyclopedia

Linux is a family of open source Unix-like operating systems based on the Linux kernel, an operating system kernel first released on September 17, 1991 by Linus Torvalds. Linux is typically packaged in a Linux distribution (or distro for short).

Distributions include the Linux kernel and supporting system software and libraries, many of which are provided by the GNU Project. Many Linux distributions use the word “Linux” in their name, but the Free Software Foundation uses the name GNU/Linux to emphasize the importance of GNU software, causing some controversy.

Rules

  • Posts must be relevant to operating systems running the Linux kernel. GNU/Linux or otherwise.
  • No misinformation
  • No NSFW content
  • No hate speech, bigotry, etc

Related Communities

  • !opensource@lemmy.ml
  • !libre_culture@lemmy.ml
  • !technology@lemmy.ml
  • !libre_hardware@lemmy.ml

Community icon by Alpár-Etele Méder, licensed under CC BY 3.0

Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 229 users / day
  • 1.02K users / week
  • 2.7K users / month
  • 6.27K users / 6 months
  • 1.31K local subscribers
  • 67.8K subscribers
  • 8.08K Posts
  • 108K Comments
  • Modlog
  • mods:
  • AgreeableLandscape ( AgreeableLandscape@lemmy.ml ) 
  • nooter692 ( nooter692@lemmy.ml ) 
  • MarcellusDrum ( MarcellusDrum@lemmy.ml ) 
  • Arthur Besse ( cypherpunks@lemmy.ml ) 
  • Cyclohexane ( cyclohexane@lemmy.ml ) 
  • d3Xt3r ( d3Xt3r@lemmy.nz ) 
  • BE: 0.19.15
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code