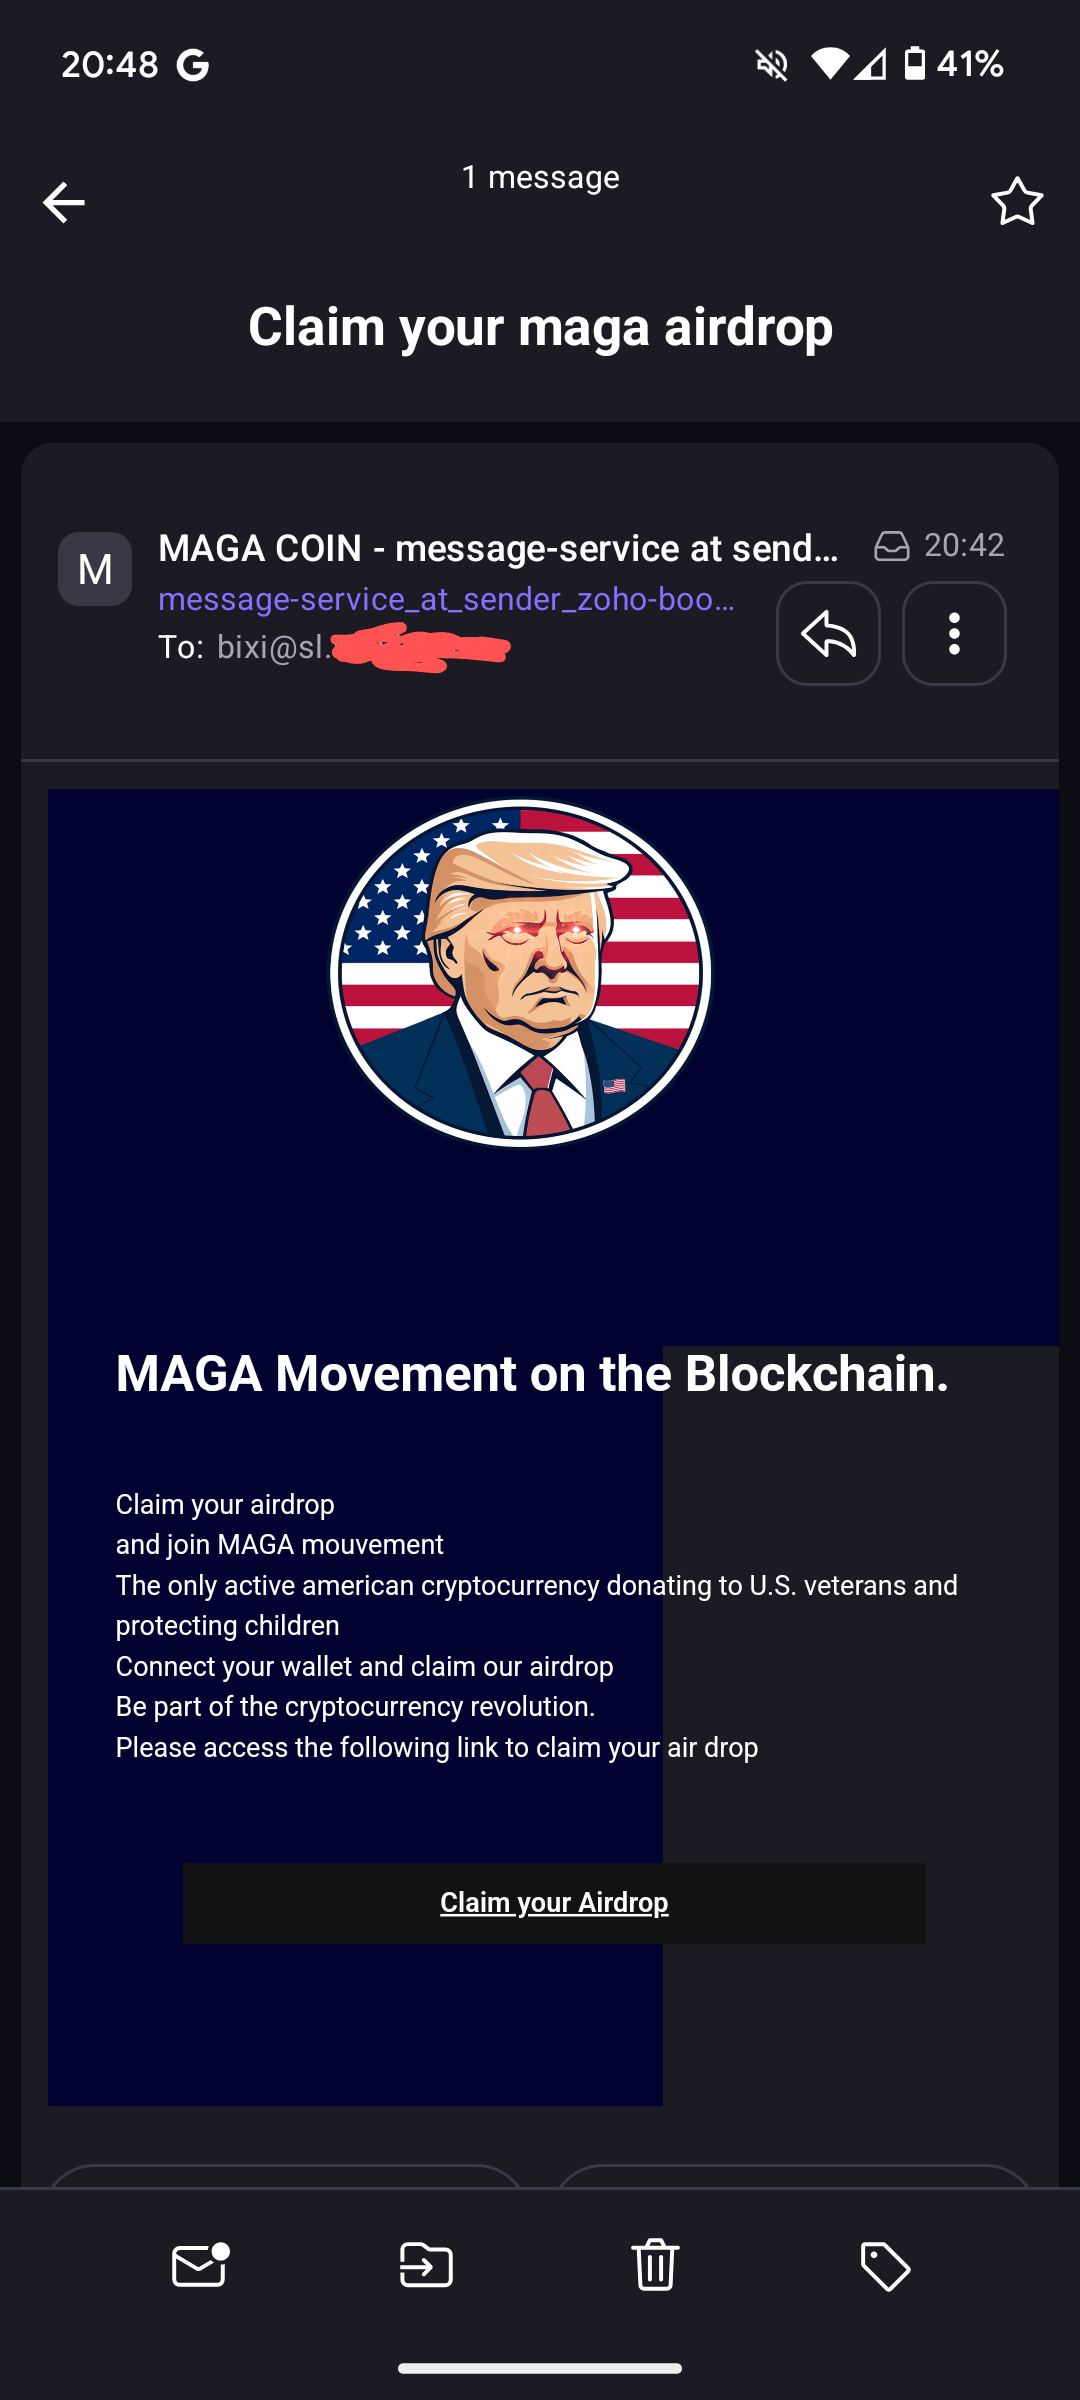
I know this because I use SimpleLogin to provide each service with its own specialized email address. You can see in the picture the address starts with bixi@sl.***
It’s also possible but unlikely that they sold user data.
I also assign unique eMail addresses for my online accounts, and also got this eMail today.
It’s likely that Bixi got hacked, not that they sold the eMail address.
Just do what I do – change the eMail address slightly on the mail server and on your online account.
Oh yeah absolutely, it was just concerning to me that Bixi of all people would let my email address loose.
I think it’s more likely they got breached, or a third-party was breached (I see “zoho” in there). It’s easy for companies with shitty code to leak things like SendGrid tokens and web scrapers pick them up and use them for shit like the email you got.
I do the same thing for my emails, it’s wild to trace back who leaked my email addresses. Man I hate how lousy our tech security is these days, or rather, the lack of fucks given and the lack of protections for consumers. Companies would rather buy cybersecurity insurance than actually make their shit secure.
I just checked some older eMails, and it’s not their mail provider / API token that got breached (previous messages used cyberimpact, not zoho).
This is probably the case, I’ve updated my title.
This is not sufficient for your conclusion given the burden of proof required for this claim. And, to be clear, you are claiming that: This organization controlled by the municipality is SELLING your email address. Your proof is a screenshot with the addressed censored. Not that there was a leak, not that someone guessed this handle, not that PBSC got hacked, not that you typed the wrong handle into a form. I can run this past bixi for you if you DM me your address, but you’re assuming a lot and I would bet not just MAGA but real coins that you’re wrong about bixi selling your info.
That’s a fair point, it’s totally possible they got breached, I’ll update my title / desc accordingly :)
Btw, as far as I know, Bixi is owned by Lyft and not the municipality, but feel free to correct me.
Btw I contacted them by email this morning and gave them all the information I have, waiting on a reply.
I sent you a PM with the information, let me know if you got it :)
I’ve gotten no response from them after a couple of days
Call em, let them know your case number, it’s what I did.
They replied to me letting me know they were looking into it after our call.
Pour ma part je n’ai pas reçu ce joli courriel. Peut-être que leur modèle de traitement pense que je suis trop pauvre pour leur arnaque 🤷
Il est possible que tu sois tombé sur une autre liste de distribution, Zoho ne semble pas être leur fournisseur courant.
Ou alors la possible fuite se serait produite avant mon inscription en 2019. C’est quand même intriguant comme situation en lien avec bixi
Impossible, ça fait moins d’un an que j’ai cette adresse courriel
Perso je pense qu’ils testent les eaux avec une petite batch avant d’envoyer une grosse batch de spam à tout le monde, voir si Bixi va s’en rendre compte.
Bon bien on va rester sur le qui-vive. On n’est pas rendu à une alerte de fuite de données personnelles près depuis quelques mois…
TicketMaster: Hold my beer
@isVeryLoud I got the same email a few days ago from my bixi-specific account. This is pretty typical of a breach, doubt they sold it as such.
Yup it is most likely a breach, I reported it to them on my side, it’d be great since you also have a single-use email address if you could also report it to them.
You can give them a call after you email them the info to get them to get on it, that’s what I did :)