It’s due to a cryptographic library implementation in a controller used in the yubikey. It’s a third party controller, and this isn’t exclusive to yubikeys either, a shitload of other stuff uses the same controller and is likely vulnerable to the same attack.
Also, the attack requires around $10k worth of equipment and physical access to the yubikey, so while a valid attack vector, it’s also not something to get into a panic about.

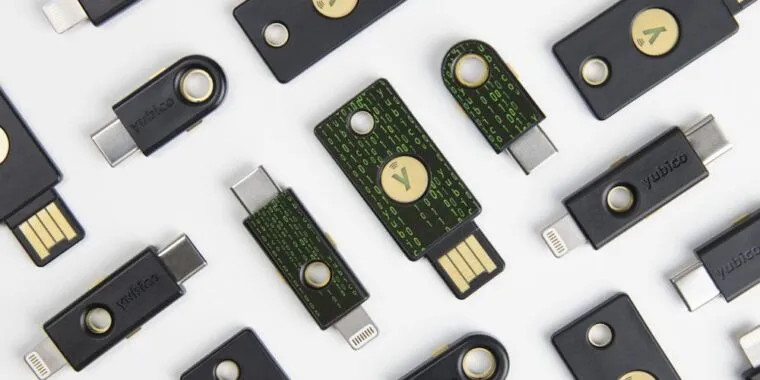
Is this because FIDO2 is flawed, the yubikey hardware design is flawed or both?
It’s due to a cryptographic library implementation in a controller used in the yubikey. It’s a third party controller, and this isn’t exclusive to yubikeys either, a shitload of other stuff uses the same controller and is likely vulnerable to the same attack.
Also, the attack requires around $10k worth of equipment and physical access to the yubikey, so while a valid attack vector, it’s also not something to get into a panic about.