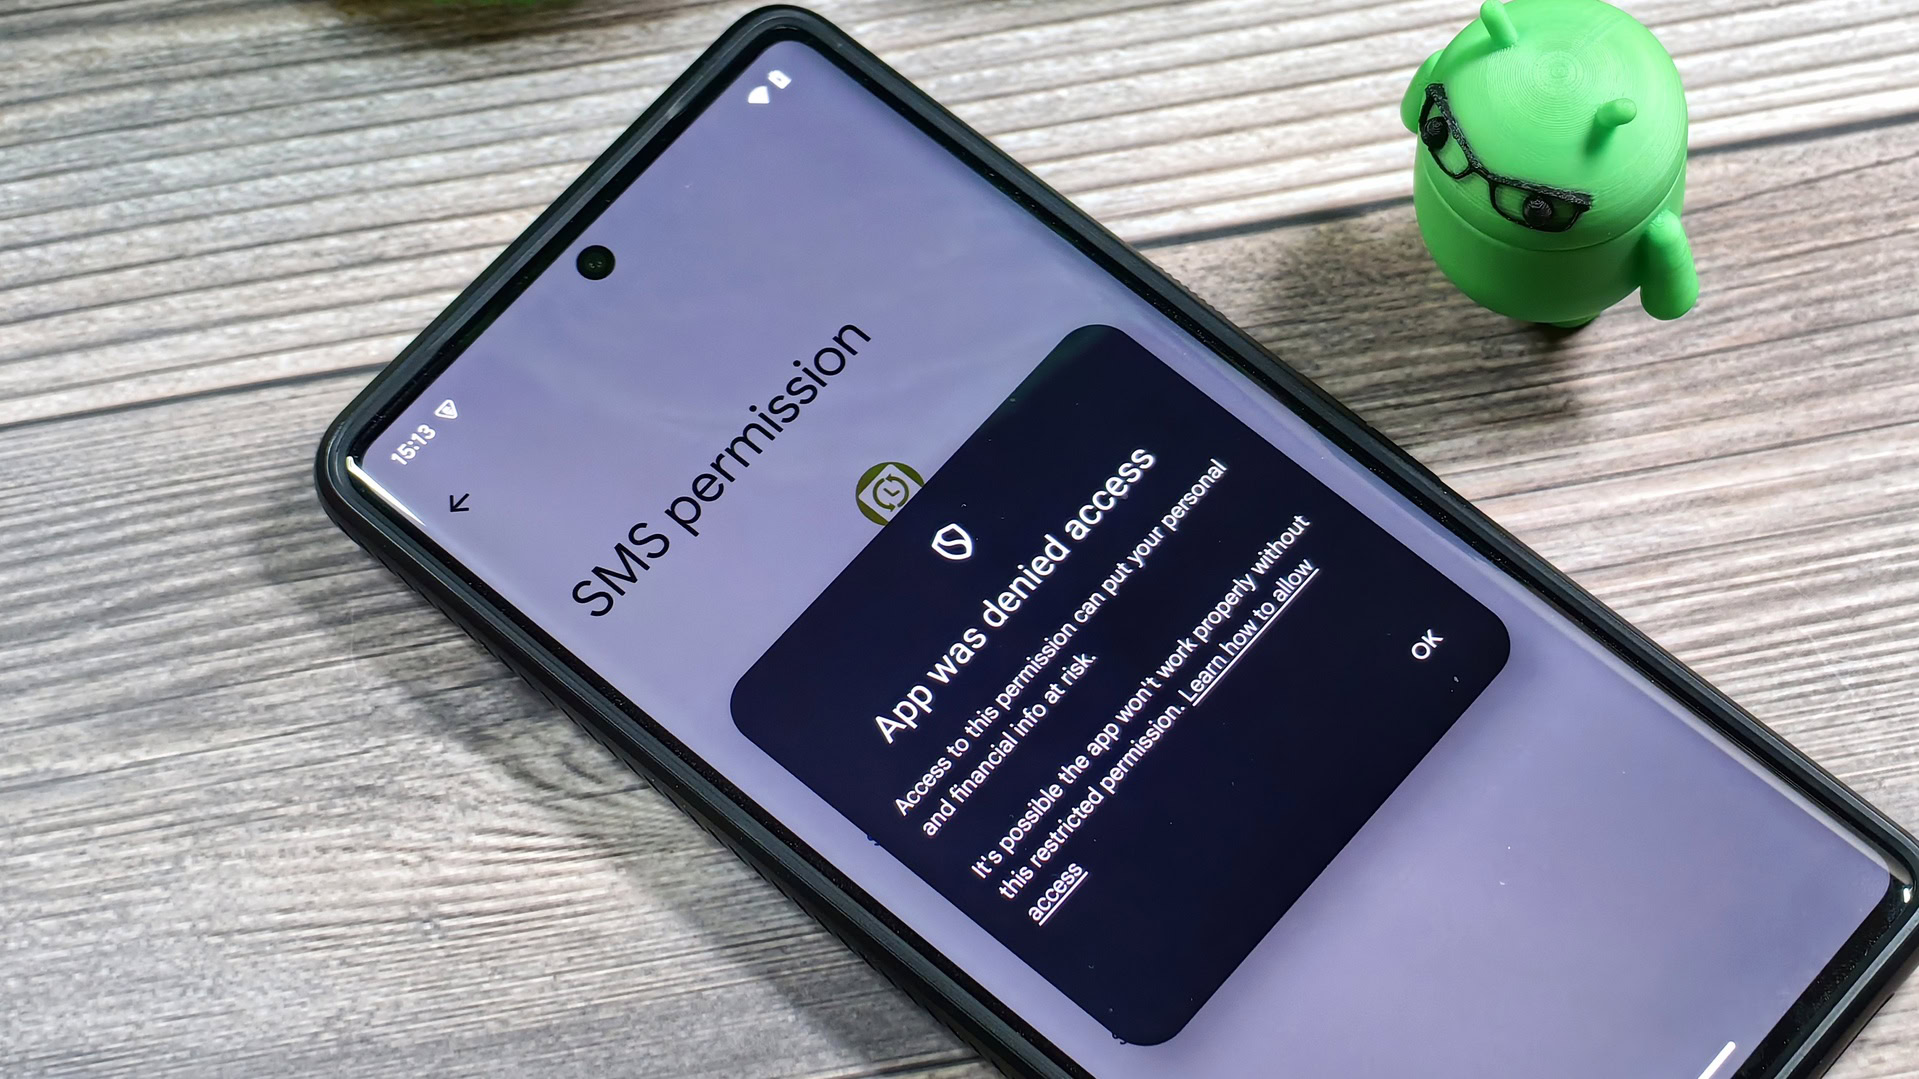
Yay, Google adding another hurdle for alternative app stores and their developers…
F-Droid store/repo is safer than Google Play Store. Google’s own store has many shady apps, including spyware and occasionnal malware.
I don’t get the argument that Play Store is safer than others.
Google play services is spyware
Sure, to make it safer in the same way Microsoft made you safer by making it harder to install Linux with UEFI.
Ridiculous, mother of bullshit! Switching to Linux appears to be the only option left for a personal computing device.
I really hope phones get better Linux support soon… it really isn’t daily driver material for most phones at the moment.
Honestly we need a community OS like Android/Chome OS
I like Linux but it would be really cool to have a OS that was less modular and more purpose built. I feel like there is enough people interested that we could raise some money to hire some developers. On think Chome OS and Android get right is the hassle free unified experience.
There’s GrapheneOS that I think would try to address this problem — secure, proper architecture, compatible with some major app stack (e.g. Android apps). It’s AOSP-based, but they’re already thinking ahead up to a point where they would be forced to fork it and even work with OEMs to create their own phone hardware for it. There are a couple of threads on their Mastodon.
I don’t know how much they would be able to achieve, but I would pay for such system.
Graphene doesn’t play nice with others
Yes, unfortunately. It’s their con, but also their pro at the same time. It’s bad because they end up isolated from everyone else playing nice with each other, and then no one wants to deal with them, but they also don’t agree on compromises that might hinder security or the stability and development of their project. And I respect that. That is partly a reason why they created probably the most secure and private AOSP distrubution nowadays.
they don’t compromises that might hinder security or the stability
I call BS on that one. It feels more to me like they are seeking power and control. They could seriously benefit from working with other projects but they don’t.
Just turn off Google Play Protect and it’ll let you sideload whatever you want.
You can’t seriously actually trust that turning it off in the Google owned app they control or update will be meaningful. I’m really sick of people claiming it is, and I hope this will get them to realize that.
If you want to crush it fully, disable google play store as a whole, and make sure to tell your friends too because if that solution doesn’t get more popular there might not be third party apps to install since the devs will just quit.
I dunno, you’re the one claiming stuff that isn’t necessarily true (yet). This is a proposed update to Google Play Protect. You don’t have to have Google Play Protect enabled, and disabling it doesn’t really impact anything unless you’re the type of person to just download an apk from unverified sources.
Where did you hear this? I’ve seen a couple of articles on this now but none of them have mentioned its specifically play protect or that it can be turned off
I keep play protect enabled in case I download anything unsafe.
Not really necessary if you limit your APK sources to trusted sources like apkmirror or github.
Github is not a trusted source. Anyone can dump apk files over there.
At some point that stops being sideloading.
In the meantime, we’re already verifying signatures for sideloaded apps. Can’t say the same about play store apps.
Glad i run only LineageOS with no gapps.
I wonder if this will do the same thing that happened to Windows when Windows 11 wouldn’t support older devices and people switched on mass to Linux.
Either way, you’re gonna have a bifurcated Android. One Android for the plebs where Google controls everything, and one Android for those who know where Google controls nothing.
Sounds like this is going to stop things like me telling my friend to install new pipe from afteroid because they can skip YouTube ads.
Great, Apple style app notarization is just about the last thing I want on my damn phone.
Year of the Linux phone in 2026?
Lmao “safer” FOH monopolistic pieces of shit.
can they not just develop a method like they do for verifying websites with an .android folder or something? requiring everyone into a centralised place is garbage.
They can, but it’s not their goal. Their goal is to have control over 99% of Android phones produced and not let their users install adblock or NewPipe, or torrent app or whatever.