Beehaw
  • Communities
  • Create Post
  • search
    Search
  • Login
  • Sign Up
cm0002 ( cm0002@suppo.fi )  to Programming@programming.dev · 9 months ago

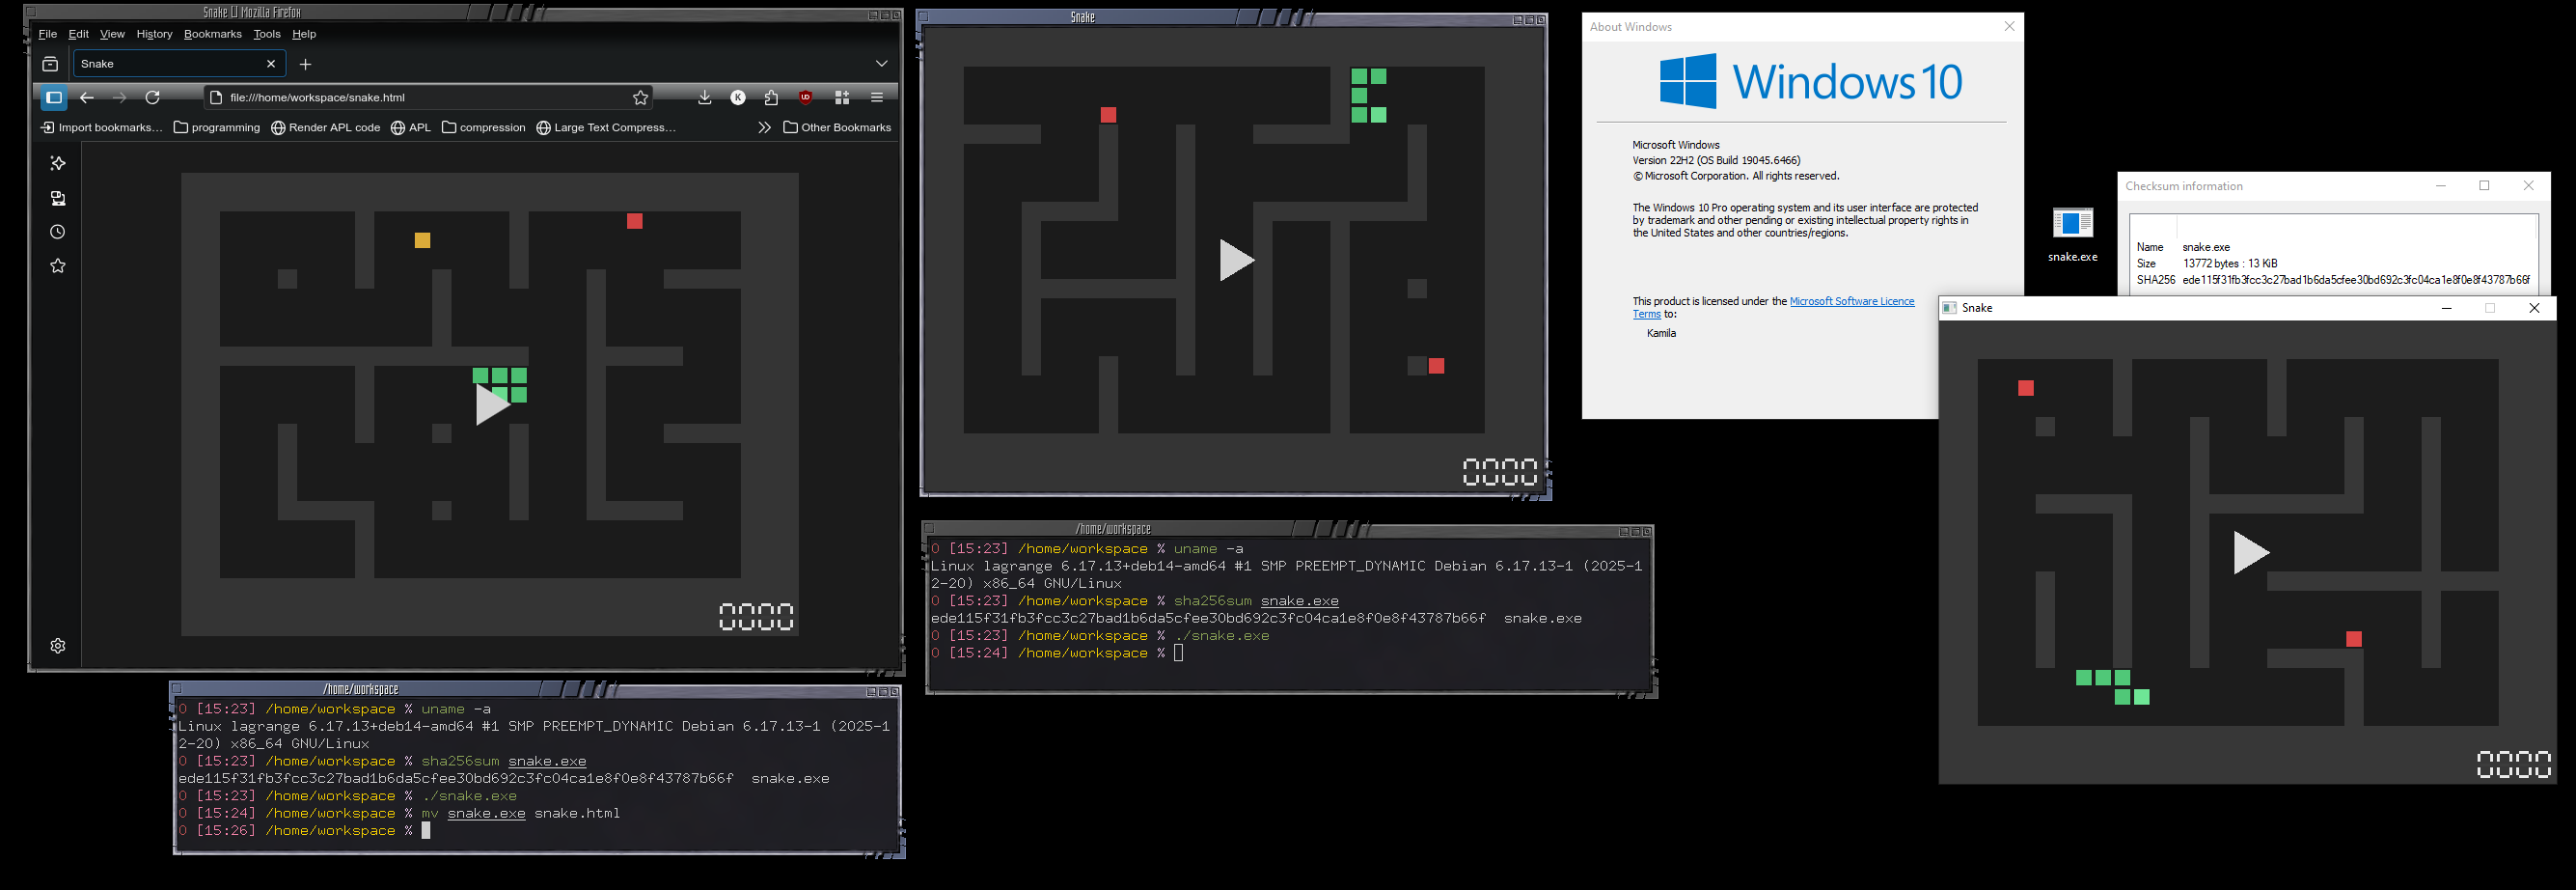
This game is a single 13 KiB file that runs on Windows, Linux and in the Browser.

iczelia.net

external-link
message-square
4
link
fedilink
  • cross-posted to:
  • programming@lemmy.ml
78
external-link

This game is a single 13 KiB file that runs on Windows, Linux and in the Browser.

iczelia.net

cm0002 ( cm0002@suppo.fi )  to Programming@programming.dev · 9 months ago
message-square
4
link
fedilink
  • cross-posted to:
  • programming@lemmy.ml
A Portable Executable (.EXE), ELF64 and HTML polyglot that runs natively on Windows, Linux and in the Browser.
alert-triangle
You must log in or # to comment.
  • jokro ( jokro@feddit.org ) 
    link
    fedilink
    arrow-up
    17
    ·
    9 months ago

    Wow, in case it’s not clear, it really is the same file for all three platforms.

  • FishFace ( FishFace@piefed.social ) 
    link
    fedilink
    English
    arrow-up
    5
    ·
    9 months ago

    Ok but is it good

  • Hirom ( Hirom@beehaw.org ) 
    link
    fedilink
    arrow-up
    4
    ·
    9 months ago

    VirusTotal doesn’t like it https://www.virustotal.com/gui/file/ede115f31fb3fcc3c27bad1b6da5cfee30bd692c3fc04ca1e8f0e8f43787b66f

    Either it’s because it’s using the same technique as malware, or because it’s malware.

    • TeamAssimilation ( TeamAssimilation@infosec.pub ) 
      link
      fedilink
      English
      arrow-up
      7
      ·
      9 months ago

      I’d guess the former, given it’s tiny compared to normal droppers, but you can never be sure these days.

      This sample is a multi-platform ‘polyglot’ binary acting as a dropper and potentially a browser-based exploit. It functions as a Windows PE (with no standard imports, suggesting custom shellcode or manual API resolution), a Linux shell script, and an HTML/JavaScript file. The Linux component contains a command (‘tail -c+4294 $0 | lzma -dc > /tmp/a’) that extracts and executes a hidden payload from its own body. The embedded JavaScript is obfuscated and uses ‘eval’ to execute dynamically generated code. This structure is typical of sophisticated malware or cross-platform exploit delivery kits.

  • MonkderVierte ( MonkderVierte@lemmy.zip ) 
    link
    fedilink
    arrow-up
    1
    ·
    9 months ago

    deleted by creator

Programming@programming.dev

programming@programming.dev

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !programming@programming.dev

Welcome to the main community in programming.dev! Feel free to post anything relating to programming here!

Cross posting is strongly encouraged in the instance. If you feel your post or another person’s post makes sense in another community cross post into it.

Hope you enjoy the instance!

Rules

Rules

  • Follow the programming.dev instance rules
  • Keep content related to programming in some way
  • If you’re posting long videos try to add in some form of tldr for those who don’t want to watch videos

Wormhole

Follow the wormhole through a path of communities !webdev@programming.dev


Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 151 users / day
  • 380 users / week
  • 1.68K users / month
  • 4.15K users / 6 months
  • 449 local subscribers
  • 28.6K subscribers
  • 2.93K Posts
  • 22.9K Comments
  • Modlog
  • mods:
  • snowe ( snowe@programming.dev ) 
  • Ategon ( Ategon@programming.dev ) 
  • UlrikHD ( UlrikHD@programming.dev ) 
  • bugsmith ( bugsmith@programming.dev ) 
  • Spyro ( Spyro@programming.dev ) 
  • BE: 0.19.15
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code