Beehaw
  • Communities
  • Create Post
  • search
    Search
  • Login
  • Sign Up
cm0002 ( cm0002@no.lastname.nz )  to Linux@programming.dev · 9 months ago

Ubuntu Pro subscription - should you pay to use Linux?

optimizedbyotto.com

external-link
message-square
22
link
fedilink
  • cross-posted to:
  • ubuntu@lemmy.ml
41
external-link

Ubuntu Pro subscription - should you pay to use Linux?

optimizedbyotto.com

cm0002 ( cm0002@no.lastname.nz )  to Linux@programming.dev · 9 months ago
message-square
22
link
fedilink
  • cross-posted to:
  • ubuntu@lemmy.ml
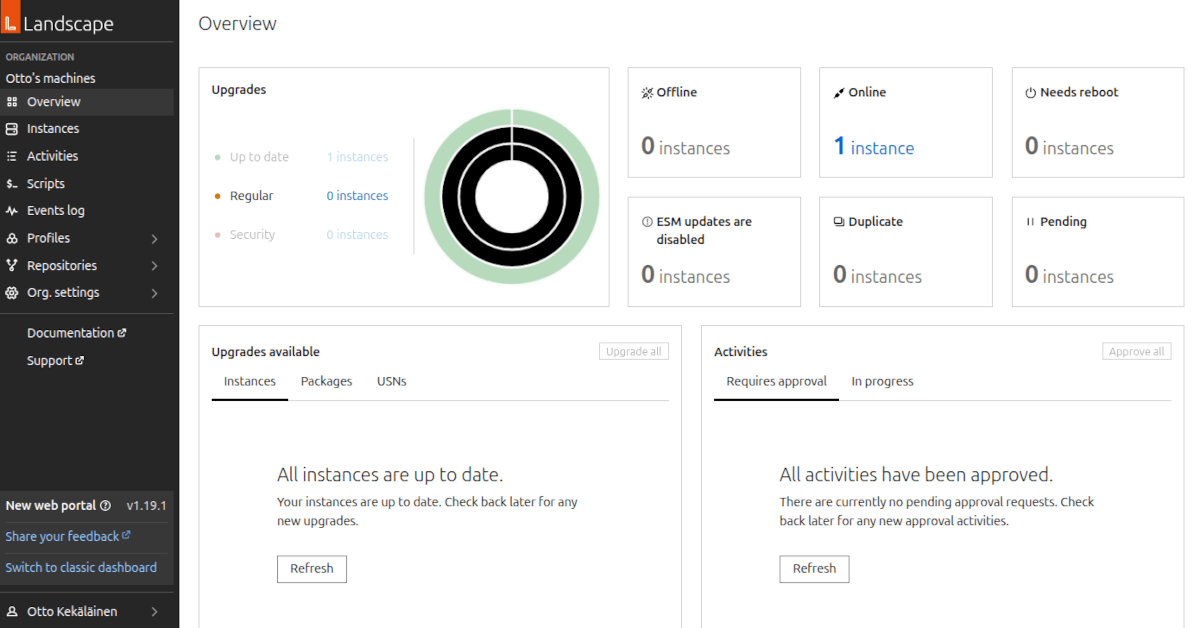
Ubuntu Pro is a subscription offering for Ubuntu users who want to pay for the assurance of getting quick and high-quality security updates for Ubuntu. I tested it out to see how it works in practice, and to evaluate how well it works as a commercial open source service model for Linux.\n
alert-triangle
You must log in or # to comment.
  • anothermember ( anothermember@feddit.uk ) 
    link
    fedilink
    English
    arrow-up
    65
    ·
    9 months ago

    Paying for services isn’t philosophically incompatible with FOSS, that’s how companies like RedHat broke through back in the day, but paying for “quick and high-quality security updates” strikes me as alarming. Am I to take from that that they’re holding back high-quality security updates from some users? Unless maybe we’re talking about extended support for EoL software.

    • shifting9810 ( shifting9810@lemmy.mrpostman.ch ) 
      link
      fedilink
      arrow-up
      29
      ·
      9 months ago

      Ubuntu Pro gives you 5 more years of security updates for versions that are EoL. You can see it here if you scroll down to the maintenance schedule https://ubuntu.com/security/esm

      • anamethatisnt ( anamethatisnt@sopuli.xyz ) 
        link
        fedilink
        arrow-up
        12
        ·
        9 months ago

        Glad to hear it’s extended maintenance for old software and not making their private users less secure.

        • Not a newt ( lemmyng@piefed.ca ) 
          link
          fedilink
          English
          arrow-up
          20
          ·
          9 months ago

          Unfortunately, it’s both. They also hold back security updates for non-latest releases that are still covered under Standard support. I work in an environment where we track new CVEs for our builds, and we constantly see vulnerabilities for 22.04 that are fixed in Pro but not made available otherwise.

          Sure, technically you can opt into Pro as an individual user without paying, but it puts everyone who uses off the shelf installs and containers at risk and is therefore an immoral and unethical process in my opinion.

          • anamethatisnt ( anamethatisnt@sopuli.xyz ) 
            link
            fedilink
            arrow-up
            7
            ·
            9 months ago

            I take it your build is dependant on the community-maintained Universe repo?
            https://ubuntu.com/security/cves/about#security
            https://help.ubuntu.com/community/Repositories/Ubuntu
            https://askubuntu.com/questions/1452497/what-are-esm-apps-and-how-do-they-relate-to-ubuntu-pro

            If they already to the work for esm-apps repo then they could at least send those fixes over to the universe repo until the release version is EoL one would think. On the other hand I have no idea what lives in universe and what lives in main.

            That was a rabbit hole.

          • ohulancutash ( ohulancutash@feddit.uk ) 
            link
            fedilink
            English
            arrow-up
            4
            ·
            9 months ago

            Pro involves Canonical making unilateral updates to certain packages, while the main universe relies on the package’s maintainers to make updates available. Unless you were to want Canonical to take over development of every bit of linux software, I don’t see how they could improve this.

          • Die4Ever ( Die4Ever@retrolemmy.com ) 
            link
            fedilink
            English
            arrow-up
            1
            ·
            9 months ago

            for 22.04

            What about 25.10?

            • Not a newt ( lemmyng@piefed.ca ) 
              link
              fedilink
              English
              arrow-up
              2
              ·
              9 months ago

              That one is not LTS, you’ll want to update to 26.04 sooner rather than later.

              • Die4Ever ( Die4Ever@retrolemmy.com ) 
                link
                fedilink
                English
                arrow-up
                1
                ·
                9 months ago

                yea I would say that’s what home users should be doing anyways? idk to me it doesn’t make sense to be so far behind on updates when the non-LTS is available

    • Bobo The Great ( bobo1900@startrek.website ) 
      link
      fedilink
      arrow-up
      3
      ·
      9 months ago

      Well, correct me if I’m wrong, but RedHat also had more recent updates compared to CentOS, while also being certified.

      • anothermember ( anothermember@feddit.uk ) 
        link
        fedilink
        English
        arrow-up
        4
        ·
        9 months ago

        None of this affects what happened “back in the day” which is what I was talking about.

        That said, my understanding of the current packaging philosophy of RHEL/CentOS Stream is that embargoed security fixes go in to RHEL first, then to CentOS Stream once the embargo is lifted (that’s pretty much as you’d expect), otherwise everything goes in to CentOS Stream first. Unless you have counter-examples I’ve not heard of?

  • nightm4re ( nightm4re@feddit.org ) 
    link
    fedilink
    arrow-up
    19
    ·
    9 months ago

    Saving you a click: No.

    • squirrel ( squirrel@piefed.kobel.fyi ) 
      link
      fedilink
      English
      arrow-up
      28
      ·
      9 months ago

      But, consider donating to your distro of choice.

  • Pommes_für_dein_Balg ( mech@feddit.org ) 
    link
    fedilink
    arrow-up
    12
    ·
    9 months ago

    TIL as a normal Ubuntu user, you don’t get quick and high-quality security updates.

    • anamethatisnt ( anamethatisnt@sopuli.xyz ) 
      link
      fedilink
      arrow-up
      16
      ·
      9 months ago

      You do, but not when your distro is EoL and not with livepatching to avoid reboots.

      • https://ubuntu.com/security/esm

      • https://ubuntu.com/pro
      • Not a newt ( lemmyng@piefed.ca ) 
        link
        fedilink
        English
        arrow-up
        4
        ·
        9 months ago

        Not true. 22.04 is not EoL and it doesn’t get all CVE patches backported unless you’re on Pro.

        • anamethatisnt ( anamethatisnt@sopuli.xyz ) 
          link
          fedilink
          arrow-up
          2
          ·
          edit-2
          9 months ago

          Huh, that was hidden deeper than I like. https://ubuntu.com/security/cves/about#security
          https://help.ubuntu.com/community/Repositories/Ubuntu
          https://askubuntu.com/questions/1452497/what-are-esm-apps-and-how-do-they-relate-to-ubuntu-pro

          edit: adding some relevant links

          • lad ( sukhmel@programming.dev ) 
            link
            fedilink
            English
            arrow-up
            2
            ·
            9 months ago

            From the link:

            Here, the Ubuntu developers roll out in-house universe security patches (additional backports of new patches against historical versions of the packages), which was previously not available

            I’m not sure every package should be considered supported in LTS, so this not being available by default looks ok for me

  • hperrin ( hperrin@lemmy.ca ) 
    link
    fedilink
    English
    arrow-up
    8
    ·
    9 months ago

    If you need what they provide, I don’t see why not. It’s great to monetarily support open source. Devs need to eat too.

  • Rekall Incorporated ( Rekall_Incorporated@piefed.social ) 
    link
    fedilink
    English
    arrow-up
    7
    ·
    9 months ago

    Seems fine, I don’t see why a home/DIY user would stay on an Ubuntu LTS release for more than 5 years.

  • magikmw ( magikmw@piefed.social ) 
    link
    fedilink
    English
    arrow-up
    3
    ·
    9 months ago

    I’d gladly pay, and I do support some foss projects.

    However I would not pay Canonical for anything. I don’t like their products or some of their practices.

  • menas ( menas@lemmy.wtf ) 
    link
    fedilink
    arrow-up
    1
    ·
    9 months ago

    We have to invest time for the helpdesk. It’s may be ours, or others (in paying for it). However, I think the Odoo experience show how much this economic model is an incentive to get the software as hard as possible to maintain.

    Maybe we sall have many cooperatives, independents or hire people instead
Linux@programming.dev

linux@programming.dev

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !linux@programming.dev

A community for everything relating to the GNU/Linux operating system (except the memes!)

Also, check out:

  • !linux_memes@programming.dev
  • !linuxphones@lemmy.ca
  • our Matrix group chat
  • !reactos@programming.dev

Original icon base courtesy of lewing@isc.tamu.edu and The GIMP

Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 210 users / day
  • 1.18K users / week
  • 2.33K users / month
  • 5.76K users / 6 months
  • 126 local subscribers
  • 15.3K subscribers
  • 4.48K Posts
  • 23.7K Comments
  • Modlog
  • mods:
  • Ategon ( Ategon@programming.dev ) 
  • adr1an ( anzo@programming.dev ) 
  • dwraf_of_ignorance ( dwraf_of_ignorance@programming.dev ) 
  • BE: 0.19.15
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code