
Damn right. And the Nixos community forums are full of people unwilling to accept this. They will gaslight you into thinking you’re the problem. “Just do this”, as I’d it’s completely obvious and you’re dumb for not realising that. Of course if they find out you have some ideological incompatibility with them, you’re out anyway.
NIXOS really needs a fork. One that embraces or rejects flakes outright. One that stops inviting ideological battles. And one that embraces documentation.
I mean, you don’t really need a fork for that. Anyone who’s motivated to actually improve the situation here, can just write appropriate documentation.
I guess, a fork would give you a new name, and therefore a clean slate where there’s not loads of contradicting information already out there. But yeah, that’s also a lot of work…
Well, I’m not in Microslop platforms, so that’s going to be difficult.
Second, the way things work in the current nix/nixos community make it easy to create a PR but very difficult to get it merged. Attempts at writing documentation are nitpicked to death, unless you belong to the privileged class of the documentation team or have merge rights on Microslop’s Github.
A fork would also give an attempt at forming a new community with different rules and focus.
You are thinking of the better alternative, guix
I’m not that much a fan of brackets and jumping through hoops to install anything non-GNU.
Do you have some specific threads in mind? Maybe I’m lucky to never click on the bad ones but my experience is that nobody is more cynical regarding Nix/NixOS jank than the long time NixOS users. You might not always get the answer you want, because it is very jank and doing some things will get you into trouble. But people pointing that out isn’t the same thing as gaslighting.
Guix SD might be worth a look, it seems to be just straight up better in many technical regards. It has no flakes, comprehensive documentation and a blessed way to manage user homes. At least as long as you don’t really need WiFi of course…
I’m using GuixSD on my desktop, and while I think it’s better in terms of creating stuff that doesn’t already exist in upstream repos, there’s so much functionality missing that’s present in nixpkgs and random flakes online that for the average person complaining about Nix jank it’s very likely not worth the effort. On the bright side they released 1.5 recently so you no longer have to use a 3 year old image (that likely doesn’t work right if your computer is too new) or a nightly one to get things running.
At least as long as you don’t really need WiFi of course…
Hey, now – the NonGuix repo. exists!
_
For those unfamiliar, it contains software with proprietary elements that otherwise can’t make it into the Guix software repository, à la
non-freefor Debian.You can get the normal Linux kernel and all the hardware compatibility you’d typically expect easily through NonGuix.
For some reason, stuff like libre wolf isn’t in the guix repo. Not even Firefox. It’s very confusing.
Firefox’s use of Encrypted Media Extensions violates the GNU Free System Distribution Guidelines as it allows for playing of DRM-protected content which can steer people to non-free software (there may be additional other reasons but that’s one I definitely know of).
But it’s perfectly available in NonGuix; I use Firefox regularly on Guix.
As for Librewolf, I’m not sure that’s accurate? I see it available in the default Guix repo.s, latest version: https://packages.guix.gnu.org/packages/librewolf/.
It was added about 2 years ago. Admittedly, Guix is a smaller distro so some packages aren’t packaged immediately just as a consequence of a lack of human resources; but it also continues to improve over time, quite nicely.
It’s been a while since I left the forums, but there always seems to be drama and something going on. I didn’t the community to be very helpful and inviting. It left a very bad taste in my mouth and in mostly avoid it. Now I ask LLMs to whip something up when in need it.
At least as long as you don’t really need WiFi of course…
I thought that was a solved problem on Linux. Is it the reluctance to use binary blobs?
I thought that was a solved problem on Linux. Is it the reluctance to use binary blobs?
Yes. For the same reason you also don’t get firmware updates on Guix. Or Firefox.
One that stops inviting ideological battles
That’s impossible IMHO. Nix is fundamentally about doing things “the right way”, and so there will always be disagreements about what “the right way” is. I think they are bound to be eventually settled on the best possible answer, you don’t need a fork for that.
If only the battles were about software. They are about unrelated beliefs and political ideologies. I’d very much prefer ideological battles about software trust me.
The problem is that NixOS achieves all of this by breaking assumptions that almost all Linux software relies on. Most Linux binaries assume the Filesystem Hierarchy Standard exists, and they expect interpreters and libraries at fixed global paths.
This is a problem of those applications, we began to make appimages that do not make those assumptions and work in NixOS directly. (And this also means it works in places like alpine where a lot of those binaries wont either).
People like to throw the FHS around but the reality is that not a single distro follows it fully, I wouldn’t rely on it to be the same in the near future at all.
Most of these are still relevant issues afaik, so yeah… appimages are just not a solution for everything. Same as stuff like flatpak and snap. These are nice for when you just need some little standalone app that doesnt do a lot of compute heavy stuff, but they will never replace native implementations.
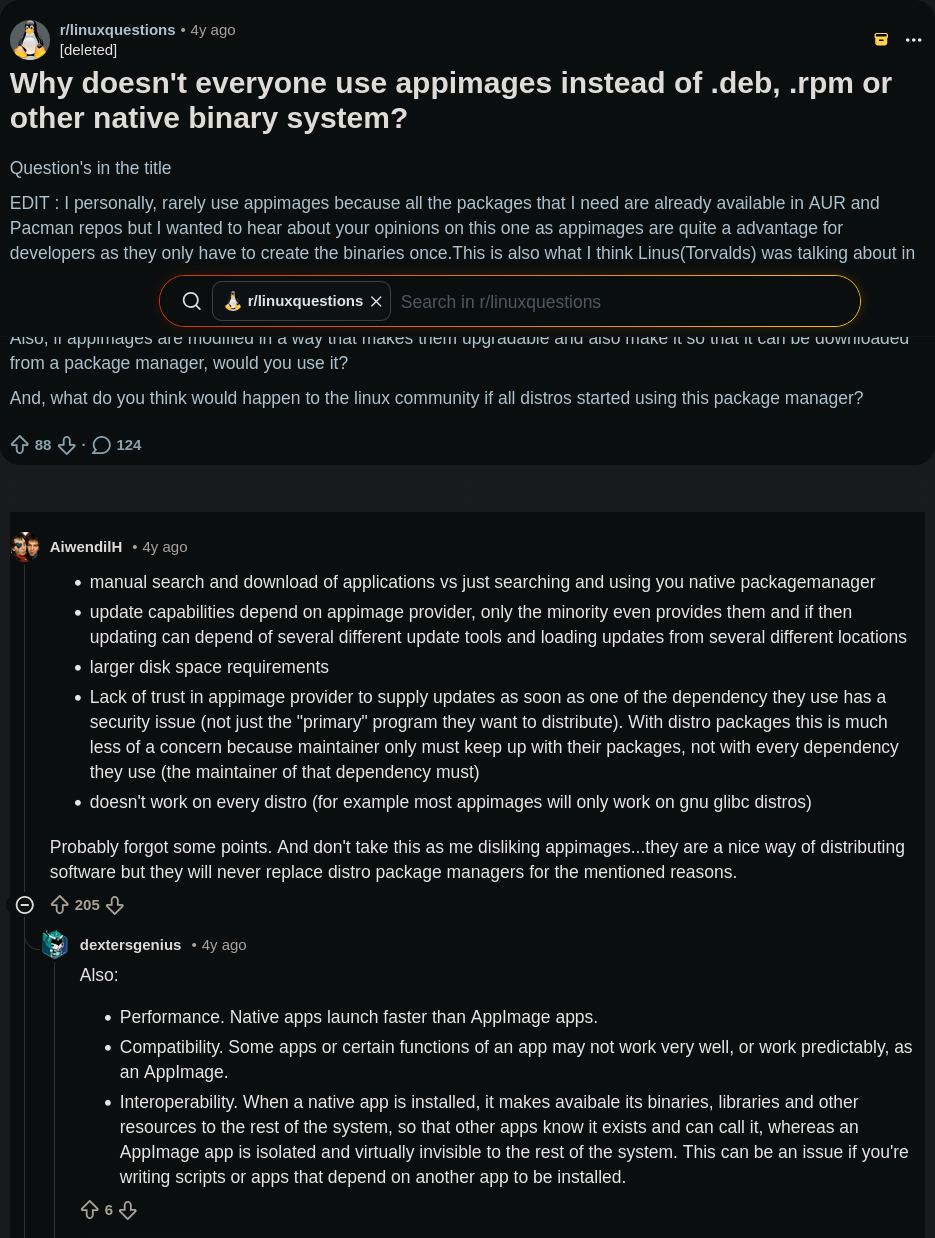
The points in the screenshot are just false and outdated, the guy even says that it doesn’t work on every distro lol
This is signal made with sharun working on ubuntu 12.04 a 14 year old distro: https://imgur.com/a/1f5S0P7 The distro is so old that internet no longer worked lol, had to use a flash drive to transfer the appimage.
we use a lot less storage than flatpak and this comparison is outdated, we have reduced the size of a lot of apps since then.
I actually did a quick test installing an alpine linux container and about 10 GUI apps vs appimage and appimage used less storage, now this comparison was flawed because I later realized that the alpine stable repo was super old and for example GIMP was pulling the gtk2 version instead of the gtk3 one (which brings all of gtk2 into the system instead of sharing the existing gtk3) but you get the idea of how close we are.
For updates and desktop integration use AM or soar
but they will never replace native implementations.
Eden makes its appimage using sharun, they made it with PGO optimizations on it which has a ~10% increase in FPS.
native implementations wouldn’t bother doing this, in fact PCSX2 had to tell people to not use the official archlinux package while it existed, because archlinux compiled it with generic flags which was horrible lol
This is also the reason why this benchmark showed appimage performing much better, you are free to optimize your application, while distros packages, flatpak, etc you often have to deal with packaging policies that do not allow this:
https://www.reddit.com/r/linux/comments/u5gr7r/interesting_benchmarks_of_flatpak_vs_snap_vs/
At this point, FHS feels more like a hindrance to me. Also, it was made in a time with very limited disk capacity and personal computers weren’t much of a thing yet.
@MonkderVierte @Samueru_sama I don’t think the standard (more like a guideline) is bad in itself: consistence of file-system use across applications is good for all our sanity. It is the assumption that all applications use it rigorously that is the problem. The word is SHOULD, not MUST.
While i agree that a standard is useful, i think the FHS is out of date: it has lot’s of fragmentation where it is not needed anymore, instead of keeping it simple. And also lots of reinterpretations, which makes it even more confusing.
Which results in some people who learned FHS thing (but never why it happened) keeping slave-ish to it and doing nonsense in major distros. Which, again, results in small niche distro being forced to it too, because they lack the manpower to adapt the tooling.
Lol love the title.
I feel the same about KDE on Wayland, it’s amazing but it’s not stable enough yet.
Took my laptop to work and it had a stroke when I plugged it into the office monitors
That’s weird.
To share a contrasting experience, I run KDE on Wayland on a laptop with two physical monitors with different rotations and three virtual monitors with different resolutions and it all Just Works.I have a Nvidia GPU, and the monitors are work are old-ish
Might be the issue 🤷♂️
I have a Nvidia GPU
Ah, well I wouldn’t blame any of your graphical issues on any Linux software then.
I’m running KDE Wayland on an AMD 9070 XT video card and I’ve absolutely no problem. Perhaps it’s your system because Wayland has been heaven. Linux is finally a modern OS.
deleted by creator
I plug in the monitor through HDMi, everything freezes.
I reboot, works fine.
I plug out the HDMI, everything freezes.
Yeah that’s a KDE classic. I think I had one KDE version a few years back that had no issues with my dock but it broke on a kernel update. Maybe it’s not entirely fair to blame KDE but I never had the same issues on GNOME, Sway or Niri…
According to my research it’s Wayland.
If you switch to X11 it should be fine. I’ve updated some configs and I think it’s stable now, but I’ll see
Which version of KDE Plasma?
Plasma 6, with GTX4070
I assume driver issues
Which Plasma 6? I’m on 6.5.5
6.4.5
chiming in as another person running KDE on wayland with no more issues than i’ve had on any other software
deleted by creator
Didn’t they start going anti-woke at some point? I was very excited about nixos when i started trying it and then between the weapons sponsorships and some anti woke stuff i read about at the time, i moved on
I’m not sure that description makes a lot of sense. Nixpkgs/NixOS is a fairly large community project. Some of the contributors are certainly anti-woke (although quite a few of those were banned from official spaces a while back), and some are MIC employees (Anduril is somewhat infamous with a seat on the so-called “steering council”). That’s not especially unusual by itself, and you can definitely do worse than “one guy is a MIC employee” (just ask the GNU or suckless folks). What is unusual is the very public meltdowns that happened surrounding it, including the moderation team resigning. The community fortunately seems to have survived all of that though.
Anyone curious can read through the most recently active governance related thread and the rest of the discourse meta category. Outside of that the subreddit had an issue with Lunduke spam at the time, but this has since died down (and the posts were removed). I don’t frequent the Matrix (official) or Discord (unofficial) so maybe those are really bad and I don’t know about it, but from my experience I honestly have little to complain about.
Having someone from the MIC with a seat on the steering council is pretty fucking damning on its own ngl
This title is exactly right
Switching is hard, but going back is impossible.
I never want to go back to an OS I can’t diff or track under revision control. I just love being able to solve an issue once and move on without worrying about if I’ll forget all the minutiae of changes I made to my customized system when it eventually comes to migrating workstations or replicating across my computers.
Personally, i dream of a stateless, tag/attribute-based, tree-less operating system. “directories” would not be neccessary but a tag could be displayed as one in file managers. Want to load a library? type:library, name:xyz it is.
Stuff is there on the disk anyway, you just have to identify it.But that would require the whole system and the tooling made for this.
But maybe we get there; since the young generation isn’t used to file trees anymore.Edit: ok, scratch the kernel, it could work.
You described a file system. You can make that system easily and put in any os. You don’t have to make and os for one feature.
But even in NixOS there are issues with non-FHS paths. And the kernel expects some paths too, also the whole bootstrapping thing. Sure, they could just be adapted.
Wouldn’t it just require a kernel module rather than a whole kernel?
I think what you’re looking for is simply an indexer + UI that sorts your filesystem by tags rather than by directory structure. Not sure if that’s as beneficial as you imagine it to be, but IIRC KDE allows you to do something like that in Dolphin.
No, they always have to keep a index uptodate. And no synch (or even compatibility) with other such tooling.Only thing that comes close currently is xattributes some fs support. But they are wholly a undefined blank slate.About advantages, no broken paths would be one.
Dolphin (well, whatever the KDE’s indexer is called) uses xattrs under the hood for tagging, so it will be compatible with other software (including {get,set}fattr).
The index has to be up-to-date, but then that would be true with any tag-based filesystem, it’s just happening on a different layer (and arguably a layer which is more suitable for this - not sure it’d be a good idea to enforce synchronous indexing during xattr writes).
The most significant user-facing obstacle is lack of software which supports this system, but I guess that shows that there’s not much desire for it in reality.
Right, i remembered KDE using xattr just after writing the answer. But still, only a KDE convention how the data is stored, not a fs convention.
But my point was, we could entirely get rid of file trees.
How many times did i wish,findslowly traversing the fs tree, that you could define a bit more details than the name and roughly if it is a file, a directory or a symlink.Working on a small trashdir shell script currently, there is a .trashinfo file with the date deleted and the last used path; that’s a hack, not a solution.
The fs index could contain things like mime type, intended use (library, executable, plaintext), advanced security context, deleted/visibility, without storing a tree the tooling has to hang on to. Finding stuff on the whole disk could be instantaneous.
And yeah, of course this would be incompatible to everything *nix and Windows currently. Which is why i think it would need to be a whole new OS (with compatibility tooling to *nix).
Current *nix kernels have a lot of Server-centric assumptions the distro tooling has to work around for desktop use anyway. The file systems also, they were made for server-centric use in times of MB, not TB. ext3/4 are just iterations over the old thing, with higher limits, better optimized algorithms, and so on.deleted by creator
it undermines decades of Unix experience
Which I don’t have. So my interest got piqued.
package everything you want to run
Sounds like a way to finally make my attempts at using Linux organized
bulletproof rollbacks
I wonder how many Nix cheerleaders are aware of OSTree based systems like Silverblue, Kinoite, Bazzite, etc? They provide the same immutability guarantees, but none of the pain and standards-defiance of NixOS.
I think Nix (the package manager) is a much stronger sell than NixOS. You can use Nix to install your apps on top of another immutable OS, whereas otherwise you might go with Flatpaks, containers, AppImages, etc. It’s certainly better than adding Homebrew or some other manager like Pacman.
For devs, Nix is nice for people who can’t or don’t want to use containers for any reason (or want to use both!). I just don’t see anyone benefiting from using NixOS except for Nix addicts.
Have you tried this? I run NixOS on my server, Aurora (immutable Fedora distro based on Universal Blue) on my desktop PCs, and this sounds very interesting. Unfortunately, it seems that this is explicitly not supported on ublue-os systems.
I haven’t actually, I just assumed it would be pretty straightforward to do, but apparently not :/
That issue is full of cringe though. Not a good look for either side, and not productive. It’s not clear whether the ublue people don’t feel like supporting it, or if it’s actually not possible due to SELinux issues.
They provide the same immutability guarantees
Not as easy to have your entire system introspectable, sharable between devices, and under the same VCS. NixOS is declarative first and foremost, and all other benefits fall out from that; immutability is just one of them.
NixOS is a hack that shoehorns existing FOSS software into what an OS should really be. I doubt we’ll get anything better for the foreseeable future, except maybe Guix.
Fuck nix and anduril, go guix!
its amusing my first/second Distro was NixOS(and i didnt know much Linux,and someone told me its a good distro)
NixOS has some neat ideas but goes to the deep end implementing a near-perfect design of those ideas. If you need those ideas, it’s really great.
I’m fantasizing about doing a lipstick-on-pig kind of a facsimile of NixOS on top of Arch Linux.
Nixpkgs and home manager on top of Arch is a nice hybrid system. I gave up on the idea for my PC because it enforces a level of tidiness that I’m not always on board with. Sometimes I do Evil Things to my computer and leave garbage lying around. It doesn’t complain, and I’d shoot it if it did
Did not know that is something people do on arch!