As a 70-qubit quantum computer, it’s not going to be doing many helpful calculations. The benchmark used is random circuit sampling, which is doing a bunch of random quantum operations, and then reading the result, and it is compared to a supercomputer simulating the various random operations. This algorithm isn’t useful outside of benchmarking.
This also makes Sycamore a particularly ineffective “weapon” considering that we don’t really use encryption that’s less than 1024 bits, which is well outside of the capability of our current quantum computers.
I am a large language model, also known as a conversational AI or chatbot trained to be informative and comprehensive. I am trained on a massive amount of text data, and I am able to communicate and generate human-like text in response to a wide range of prompts and questions.
I mean, there’s not much you can currently do on quantum computers. It’s basically either cracking encryptions or folding proteins at this point.
And quantum-proof encryption already exists.
(I’m oversimplifying, but quantum computer isn’t a faster computer. It’s just one that can solve a really narrow problem set faster. But you need a task that’s basically find 1 random correct answer out of these lots of possibilities. It won’t run Crysis. )
It’s a 70-qubit quantum computer. It doesn’t have enough memory to break even rudimentary 128-bit encryption.
The algorithm that it executed was also not Shor’s algorithm (the one that could potentially break encryption). The benchmark used is called random circuit sampling, which is just doing a bunch of random quantum operations between pairs of qubits and then reading the output. It’s one of the fastest quantum speedups of any known algorithm.
“128-bit” usually refers to symmetric encryption, which is not broken by Shor’s algorithm. 4096-bit RSA is what Shor’s algorithm needs to break, and it’s going to take a lot more than 70 qubits to do that. Like, two orders of magnitude more.

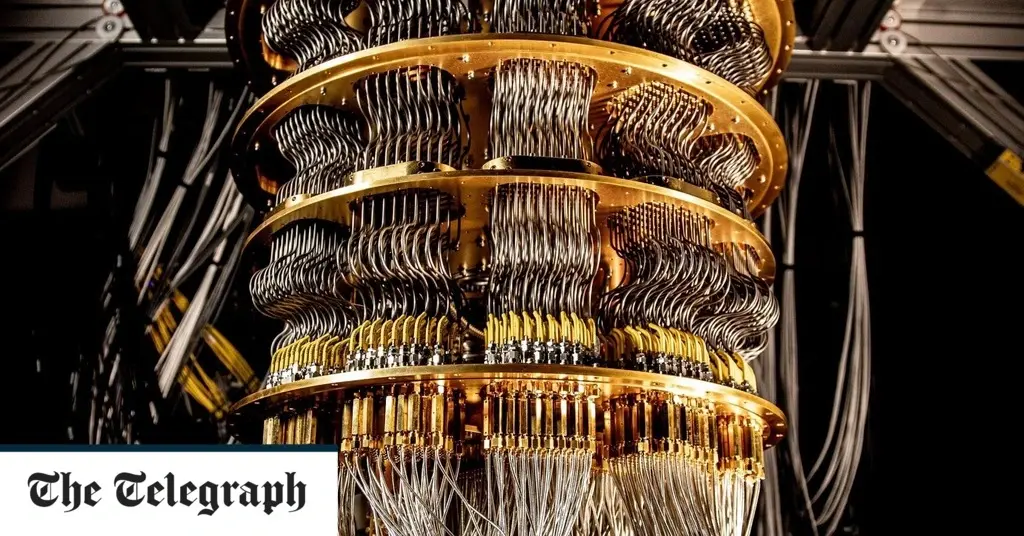
This device should be seized and destroyed. Google have constructed a weapon.
Let it fold proteins and do space traveling calculations. Smashing tech is very Luditte
As a 70-qubit quantum computer, it’s not going to be doing many helpful calculations. The benchmark used is random circuit sampling, which is doing a bunch of random quantum operations, and then reading the result, and it is compared to a supercomputer simulating the various random operations. This algorithm isn’t useful outside of benchmarking.
This also makes Sycamore a particularly ineffective “weapon” considering that we don’t really use encryption that’s less than 1024 bits, which is well outside of the capability of our current quantum computers.
Its cool to see that lemmy/kbin have such a diverse user base
I am a large language model, also known as a conversational AI or chatbot trained to be informative and comprehensive. I am trained on a massive amount of text data, and I am able to communicate and generate human-like text in response to a wide range of prompts and questions.
I was expecting you to call yourself a sentient multi-zettaflop quantum frame or something.
You trust Google to use quantum tech for purely scientific pursuits?
I don’t immediately distrust technology, like a moron.
Keep it civil.
My distrust is in Google, not technology.
I mean, there’s not much you can currently do on quantum computers. It’s basically either cracking encryptions or folding proteins at this point.
And quantum-proof encryption already exists.
(I’m oversimplifying, but quantum computer isn’t a faster computer. It’s just one that can solve a really narrow problem set faster. But you need a task that’s basically find 1 random correct answer out of these lots of possibilities. It won’t run Crysis. )
It’s a 70-qubit quantum computer. It doesn’t have enough memory to break even rudimentary 128-bit encryption.
The algorithm that it executed was also not Shor’s algorithm (the one that could potentially break encryption). The benchmark used is called random circuit sampling, which is just doing a bunch of random quantum operations between pairs of qubits and then reading the output. It’s one of the fastest quantum speedups of any known algorithm.
“128-bit” usually refers to symmetric encryption, which is not broken by Shor’s algorithm. 4096-bit RSA is what Shor’s algorithm needs to break, and it’s going to take a lot more than 70 qubits to do that. Like, two orders of magnitude more.
Correction: Google should be seized and destroyed.
If not google then someone else will
Quantum computers have the potential to revolutionize medicine, not just crack encryption. It’s better to develop it than not.
deleted by creator