
If models are trained on data that it would be a security breach for them to reveal to their users, then the real breach occurred at training.
now you know that and i know that,
The big LLMs everyone’s talking about and using are just advanced forms of theft
Sloppy LLM programming? Never!
In completely unrelated news I’ve been staring at this spinner icon for the past five minutes after asking an LLM to output nothing at all:
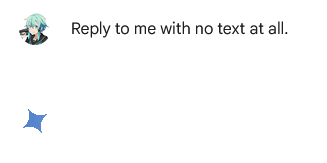
same energy as “your request could not be processed due to the following error: Success”
What are the chances that the front end was not programmed to handle the LLM returning an empty string?
Quite likely yeah. There’s no way they don’t have a timeout on the backend.
boooo Gemini now replies “I’m just a language model, so I can’t help you with that.”
“what would a reply with no text look like?” or similar?
what would a reply with no text look like?
nah it just described what an empty reply might look like in a messaging app
they seem to have done quite well at making Gemini do mundane responses
that’s a hilarious response (from it). perfectly understand how it got there, and even more laughable
deleted by creator
LLM vendors are incredibly bad
at responding to security issuesMy NSFW reply, including my own experience, is here. However, for this crowd, what I would point out is that this was always part of the mathematics, just like confabulation, and the only surprise should be that the prompt doesn’t need to saturate the context in order to approach an invariant distribution. I only have two nickels so far, for this Markov property and for confabulation from PAC learning, but it’s
completely expectedweird that it’s happened twice.These guys got barely enough staff to run the model lol