Use Aegis.
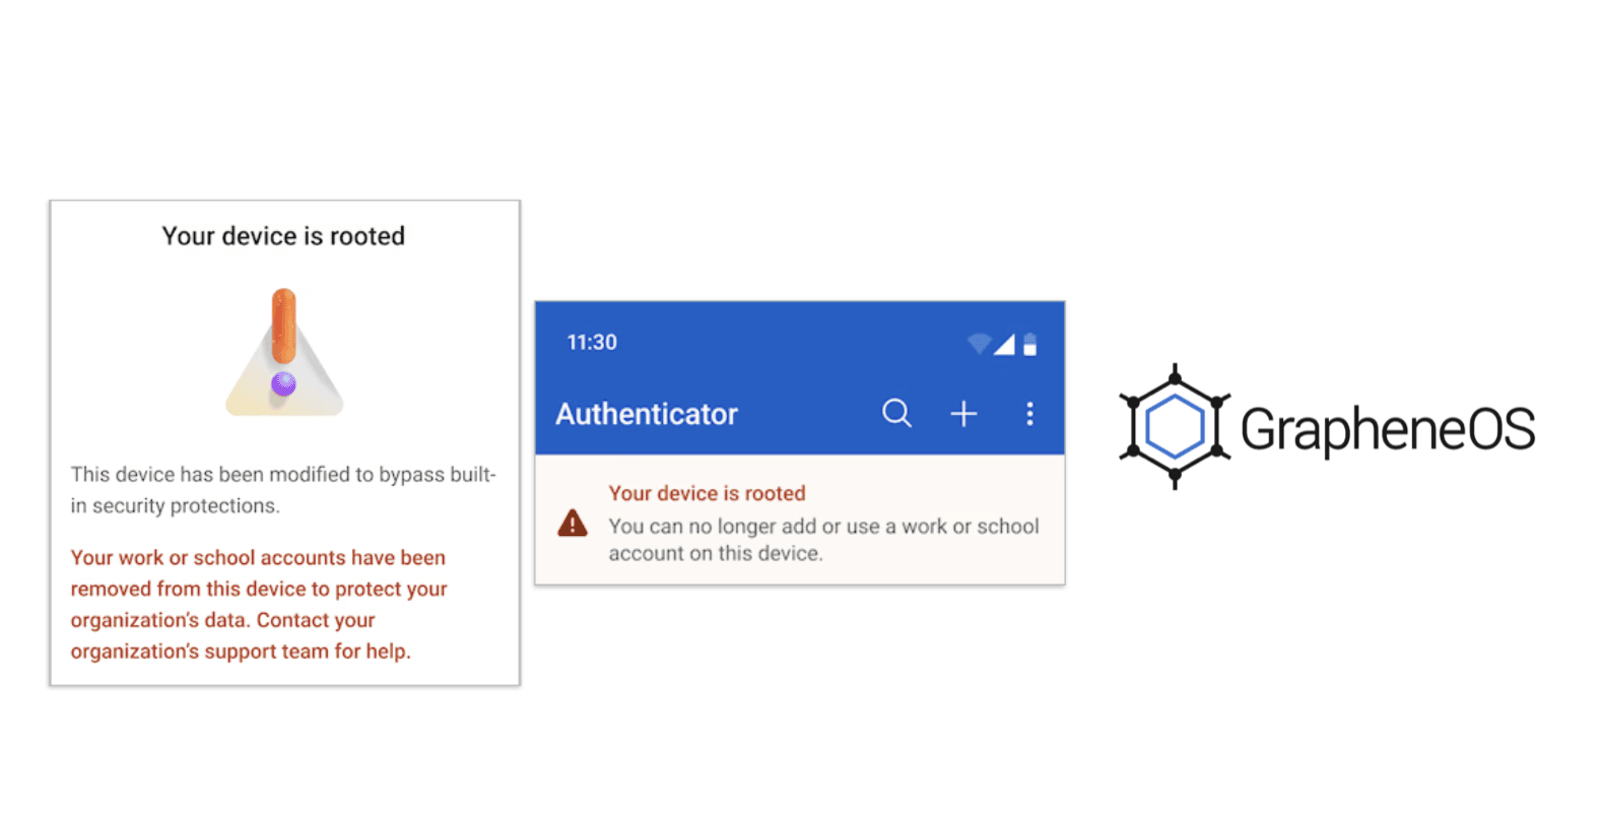
The MS Authenticator contains analytics & telemetry & way too many permissions and should not be used: https://reports.exodus-privacy.eu.org/en/reports/com.azure.authenticator/latest/ (it looks more like a scam than legitimate, but that’s exactly what Microslop is in 2026…)
For comparison, Aegis is a legitimate app that only does what it should do: https://reports.exodus-privacy.eu.org/en/reports/com.beemdevelopment.aegis/latest/#permissions
Any other authenticator also works with any MS service so there’s no reason at all to use the MS Authenticator unless you like handing over more data to MS for no reason. EDIT: According to comments, your company might have the option to enforce usage of MS Authenticator only. But this doesn’t seem to be the default, at least in Germany where I’ve heard from 2 sources that they can use any authenticator app for M365 for example.
By the way, Graphene OS is NOT rooted, but what does truth or sane app behavior even mean anymore for Microslop in 2026… Just stop using that garbage.
Not entirely true, I can’t use Stratum for work. It’s locked to MS Authenticator. My solution is to not use phone authentication as a backup. If my Yubikey dies, oh well, can’t work for a bit.
Similarly, I tried to add Outlook and Teams to a profile in Graphene. Once again, wouldn’t work because it relies on special sauce in the Android work profile. Once again, oh well, guess I’ll never ever be reachable when I’m away from my work computer.
I think I’m better off :)
deleted by creator
Yeah, and Microsoft policy is just about rooted phones.
There isn’t any reason to mention GrapheneOS, unless it is to generate unwarranted outrage.
Which seems to be working on a lot of folk on here.
They way Microsoft is checking for root won’t work on GrapheneOS since its done through Google play services, similar to the bank apps. It doesn’t matter if it’s rooted.
Interesting considering grapheneOS does not actually support rooting.
Which means the entire article is bullshit.
It literally states that Microsoft changes its policy to not allow rooted devices. So GrapheneOS has nothing to worry. It doesn’t affect them. Why does the article mention it then at all?
Seems like a clickbait article
Which means the entire article is bullshit.
Not necessarily. It could just be that Microsoft’s “root” detection is misnamed or poorly implemented. They would not be alone in either case.
Unless on Motorola devices (soon).
I hope it’s like FairPhone where you get to choose android or Murena/e/
We wouldn’t want any Graphene OS device to fulfill the requirements necessary to be certified. That would make it useless.
‘Rooted’ doesn’t mean rooted, it means the Google API it checks against says no. And is unlikely to say yes on any device that isn’t ‘official Android’, with Google Apps having System access.
Googles been getting in trouble for requiring Google apps to he certified. So maybe they allow grapheneos through to say see we don’t knowing it well be very niche.
Like my other comment said to someone else, so much for Android “OPEN SOURCE” Project, huh? Only OK if its stuffed with Google shit to make money from?
Fuck em. I just got grapheneOS and I advised my workplace we will need a workaround for authenticator.
Cool, the fewer people using Microslop apps, the better.
Honestly thank you for posting this. Lest I would’ve lost my Google and Microslop account.
Use your work phone.
I don’t need a Microsoft account and if Google insists, I will kill my account with them as well.
Fuck Microslop and fuck Google.
That’s cool. Guess my company is going to have to send me a new phone.
Oh this is some bullshit. Anyone know of a decent FOSS(ish) alternative?
I’ve heard Aegis being mentioned.
Yes I love Aegis.
ive used it for months, no issues at all
Used for years. The best.
Ente Auth
Microslop Authenticator might exclude GrapheneOS in the future due to root detection
So don’t have a rooted GrapheneOS and everything will be fine.