Beehaw
  • Communities
  • Create Post
  • search
    Search
  • Login
  • Sign Up
floofloof ( floofloof@lemmy.ca )  to cybersecurity@infosec.pub · 6 days ago

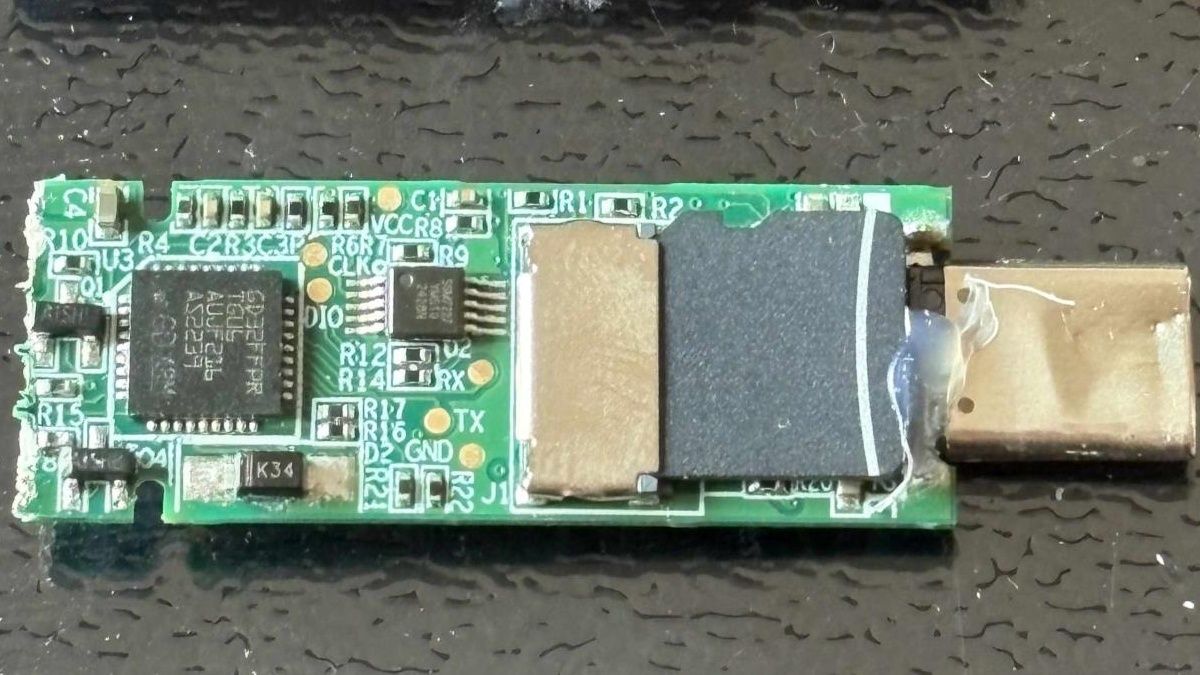
Lenovo's 'encrypted' fingerprint USB drive is just an unencrypted SD card in a fancy case

www.tomshardware.com

external-link
message-square
18
link
fedilink
107
external-link

Lenovo's 'encrypted' fingerprint USB drive is just an unencrypted SD card in a fancy case

www.tomshardware.com

floofloof ( floofloof@lemmy.ca )  to cybersecurity@infosec.pub · 6 days ago
message-square
18
link
fedilink
Lenovo's 'encrypted' fingerprint USB drive is just an unencrypted SD card in a fancy case — AI-assisted follow-up finds a backdoor and hardcoded keys in other ‘secure’ USB products (updated)
www.tomshardware.com
external-link
The fingerprint only switched the USB connection on; nothing on the card was encrypted.
alert-triangle
You must log in or register to comment.
  • fonix232 ( fonix232@fedia.io ) 
    link
    fedilink
    arrow-up
    16
    ·
    6 days ago

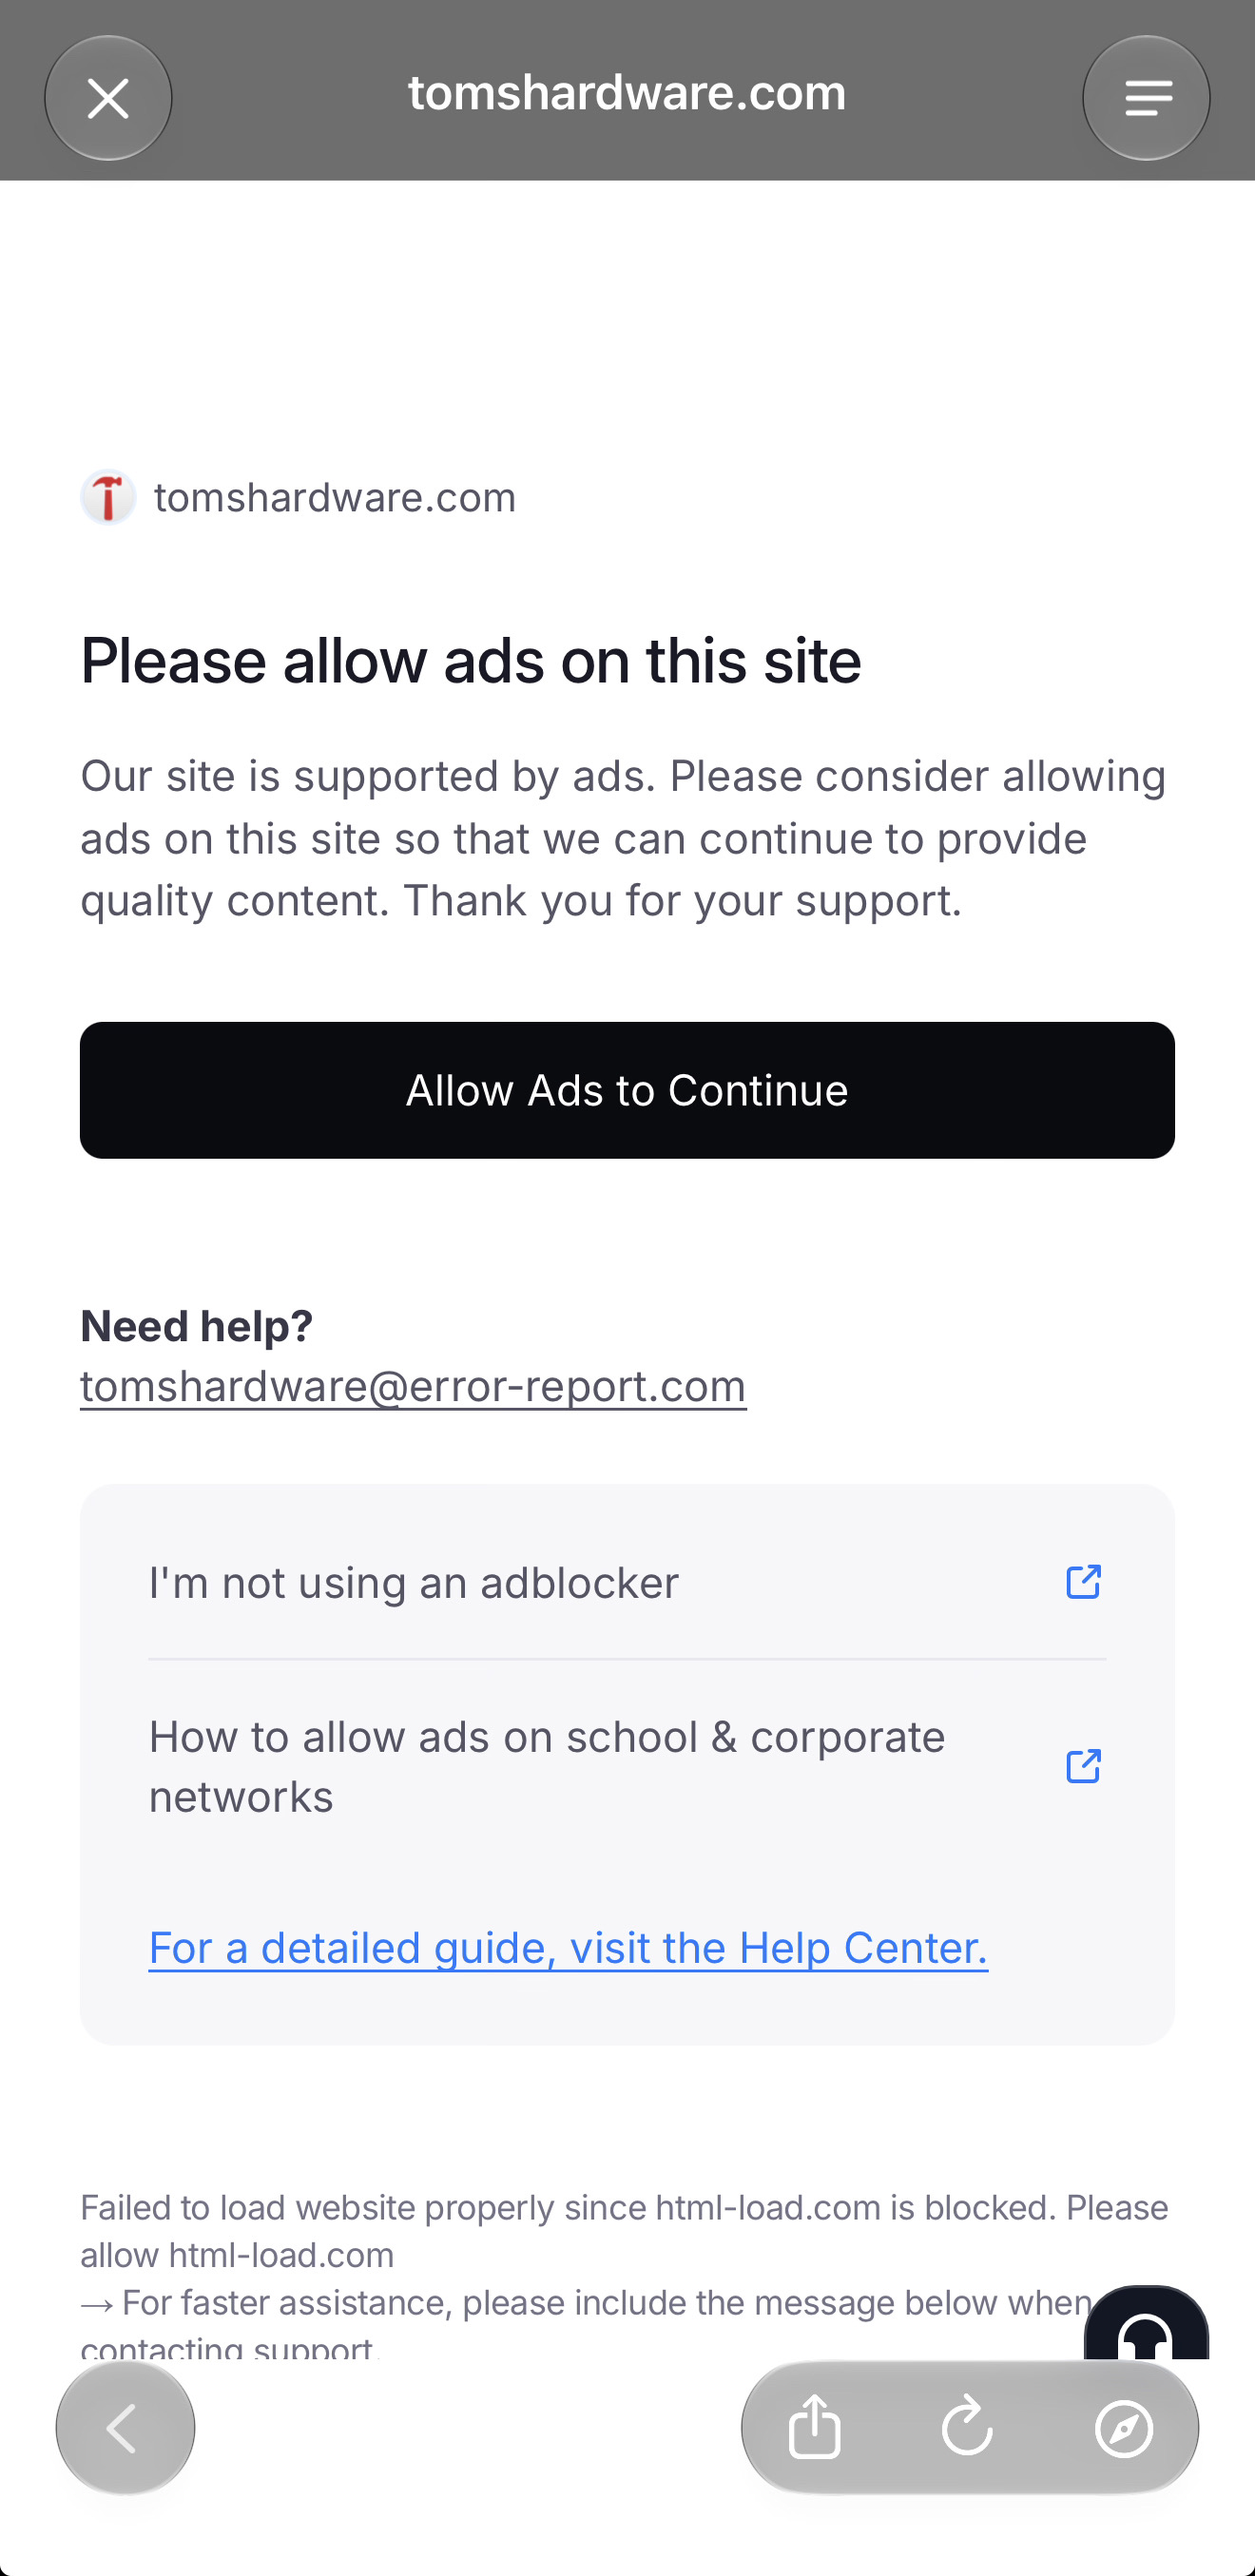
    can we PLEASE stop linking stuff from shit-ass sites that use quasi-malware services like Ad-Shield (the service behind the notorious html-load(dot)com, error-report(dot)com etc.)?

    These sites intentionally break and block access when a DNS based ad blocker is used. Not because the site can’t load - it actually loads perfectly fine behind the blockout - but because these fuckers intentionally unload CSS to break the site if ads won’t load… via the same exact methods web malware loads malicious scripts.

    • floofloof ( floofloof@lemmy.ca ) OP
      link
      fedilink
      arrow-up
      3
      ·
      6 days ago

      I have some heavy DNS filtering and the site still loads fine in Vanadium on GrapheneOS. Many sites refuse to load in the way you describe and it is annoying, but I didn’t know this site was doing that.

      • fonix232 ( fonix232@fedia.io ) 
        link
        fedilink
        arrow-up
        1
        ·
        6 days ago

        Interesting.

        I run my own AGH gateway at home with pretty heavy filtering, plus my iDevices have a NextDNS profile installed - and now most big tech sites do this crap…

        • kieron115 ( kieron115@startrek.website ) 
          link
          fedilink
          arrow-up
          1
          ·
          5 days ago

          If you use a script blocker (such as UBO) those stupid error pages tend not to work. Not helpful for any unrooted devices, I know, just throwing it out there.

          • fonix232 ( fonix232@fedia.io ) 
            link
            fedilink
            arrow-up
            1
            ·
            5 days ago

            Sadly not an option on iOS.

        • MonkderVierte ( MonkderVierte@lemmy.zip ) 
          link
          fedilink
          arrow-up
          1
          ·
          6 days ago

          Sounds to me like you accidentally have a cdn on the list? And can confirm, works for me (but i have usercss for TH anyway; their desktop-layout sucks).

          • fonix232 ( fonix232@fedia.io ) 
            link
            fedilink
            arrow-up
            3
            ·
            6 days ago

            For further information:

            html-load(dot)com, error-report(dot)com are domains owned by Ad-Shield and similar “as recovery” services that:

            • inject a script into the site from its own host
            • script checks if ad blocs load content or not
            • if no ad content is loaded, they phone home to html-load(dot)com or a similar address (making it appear to the average user that they’re some “core internet service”)
            • id html-load or their other domains aren’t reachable (they send a keyed request so it’s not as easy as having your own server respond with an empty {} script), the site will unload CSS and deliver a blocking view
          • fonix232 ( fonix232@fedia.io ) 
            link
            fedilink
            arrow-up
            2
            ·
            6 days ago

            • MonkderVierte ( MonkderVierte@lemmy.zip ) 
              link
              fedilink
              arrow-up
              1
              ·
              5 days ago

              So it’s a geoip thing? Maybe because GDPR that i don’t get it?

          • fonix232 ( fonix232@fedia.io ) 
            link
            fedilink
            arrow-up
            2
            ·
            6 days ago

            No, the block is very specifically about ad recovery via html-load(dot)com…

    • wyldrstallyns ( wyldrstallyns@lemmy.dbzer0.com ) 
      link
      fedilink
      arrow-up
      2
      ·
      6 days ago

      Isn’t there a uB or *monkey script that nips those in the bud? 🤞🏼

      • fonix232 ( fonix232@fedia.io ) 
        link
        fedilink
        arrow-up
        3
        ·
        6 days ago

        Neither of which are available on iOS in non-Safari browsers

        • wyldrstallyns ( wyldrstallyns@lemmy.dbzer0.com ) 
          link
          fedilink
          arrow-up
          2
          ·
          6 days ago

          Ah, sorry. I had no idea. 😅

  • Triumph ( Triumph@fedia.io ) 
    link
    fedilink
    arrow-up
    13
    ·
    6 days ago

    Wait wait - is it also advertised as a 1TB card that’s configured to show 1TB of space when you plug it in, but then it’s really just a 4GB card?

    • Sturgist ( Sturgist@piefed.ca ) 
      link
      fedilink
      English
      arrow-up
      3
      ·
      6 days ago

      it’s really just a 4MB card?

  • degen ( degen@midwest.social ) 
    link
    fedilink
    arrow-up
    9
    ·
    6 days ago

    an interim fix using epoxy over the card.

    Lmao encase that shit. Bro, we just need more physical security, trust me.

    • lurch (he/him) ( lurch@sh.itjust.works ) 
      link
      fedilink
      arrow-up
      1
      ·
      6 days ago

      A self destruct could fix it 😆

  • MonkderVierte ( MonkderVierte@lemmy.zip ) 
    link
    fedilink
    arrow-up
    4
    ·
    6 days ago

    discovered what Li calls backdoor accounts on another maker’s drive, as well as hardcoded keys in other supposedly secure USB storage products.

    What i always say; hardware-based encryption is not secure. It’s always in the triangle between speed, security and cost, the vendors go for speed and cost.

    And then there’s stuff like this:

    but the drive sent the correct password back over USB in plain text for the software to compare, making it easy to capture

    Cookie-cutting on the developer side.

cybersecurity@infosec.pub

cybersecurity@infosec.pub

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !cybersecurity@infosec.pub

An umbrella community for all things cybersecurity / infosec. News, research, questions, are all welcome!

Community Rules

  • Be kind
  • Limit promotional activities
  • Non-cybersecurity posts should be redirected to other communities within infosec.pub.

Enjoy!

Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 9 users / day
  • 292 users / week
  • 585 users / month
  • 1.06K users / 6 months
  • 74 local subscribers
  • 6.61K subscribers
  • 1.05K Posts
  • 1.72K Comments
  • Modlog
  • mods:
  • shellsharks ( shellsharks@infosec.pub ) 
  • tweedge ( tweedge@infosec.pub ) 
  • BE: 0.19.21
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code