I am a firm believer that there are many privacy techniques you should focus on before encrypted messaging because they will offer you much more “bang for your buck,” things like good passwords, two-factor authentication, and even encrypted email. That said, I still believe that encrypted messaging is a critical part of a well-rounded privacy and security strategy. While the vast majority of our day-to-day conversations may be benign, it can still offer a lot of insight into who we are as people – our routines, likes, and personal thoughts. This information – mundane or not – is worth protecting.
You must log in or # to comment.
XMPP, for example, does not enable end-to-end encryption by default
Why always these false myths? The most popular XMPP mobile clients do enable it by default.
It was a conscious decision for them not to enforce E2EE by default. https://web.archive.org/web/20211215132539/https://infosec-handbook.eu/articles/xmpp-aitm/
XMPP clients have like 10 different implementations because of that and are not always consistent with each other or even function universally across platforms.
But I’m not an author. That would be @nateb@mastodon.thenewoil.org.
The article you linked is a highly misleading nothing burger. And enforcing e2ee at protocol level is a bad idea for many reasons.
That’s what encrypted messagers are…
Messengers are not protocols. They use protocols. Most XMPP clients use the same encryption scheme Signal does only without being dependent on a single specific server, allowing users to spread out. I recommend reading about the differences between targeting developing a platform and developing protocols. Once you do, you’ll see XMPP+Encryption in a better light than anything like Signal. The main problem in the current moment with XMPP+Encryption us that it isn’t where the people are. Us tech weirdos can start the push into that space a little bit, but we need “Normies” to adopt to, and for that we need to be clear on what were talking about. Comparing XMPP to signal doesn’t make sense. Comparing Cheogram to Signal does. And in the latter, cheogram frankly blows Signal out of the water for real privacy and security considerations
🙄 you have obviously no idea what you are talking about.
Right? It is a generic protocol for all sorts of communications, some of which don’t require encryption. Yet every modern chat client for human-to-human communication has OMEMO, OTR, & PGP encryption options.
I immediately had my suspicions this article might contain some bullshit when I saw it was published by the new oil…
Why are we still pushing XMPP? It isn’t the 90s and I don’t feel like learning IRC 2.0.
Maybe because it works, is easy to set up, light on resources and still is evolving?
And fully open-source and relying on standards from the get go.
Gee i guess it ain’t cool, that’s why…
It isn’t easy to setup and the core protocol is dated. You can add all sorts of extensions but at the end of the day the core system is old. It feels weird to push it over Matrix. If you want something simple use IRC as you can setup encryption.
Encryption support in IRC clients is WAY behind XMPP. The one I have seen consistently is OTR in form of an add-on, and even that people rarely install. Although IRC is indeed what I prefer for public groupchats.
Matrix seems to be doing the same thing but consumes more resources. And as for setup - I have done that, it is indeed pretty easy, easier than Matrix.
What I like about Matrix so much is that it can be run fully on your own infrastructure, even the TURN server for VOIP, and you can build the clients from source yourself too.
But I agree that it’s quite difficult to use. And until now only my dad and my spouse use it with me because they love me and trust me. But they both always have problems with their clients. It randomly logs out and then they have to login with the password and with the encryption key again. For a long time calling didn’t work because I misconfigured the server. Then videos were for the longest time uploaded in full size and anything longer than a few seconds would be rejected. The whole spaces thing is implemented very weirdly so it confuses them. And then the threads are even worse so we can’t use them because nobody gets how to do it.
Signal ux is much better fyi, though I accept it’s hard to roll your own. Trade offs are generally worth
As far as I know you can’t host your own signal server which connects to their servers.
I’m using Signal with the rest of the family and most friends.
As far as I know you can’t host your own signal server which connects to their servers.
That’s right, Signal is not federated.
Yeah they killed federation, though I can’t disagree with the reason. Thankfully you don’t need to trust the server
You can technically set it up base on the published code, but you’d need to modify the client as well. Not like it’s Matrix or XMPP, asking you for server address upon registration. I am afraid to think how much of the server dependence is hardcoded there…
Use Simplex Chat instead
The downside with Simplex Chat is that there is no server side accounts
Matrix doesn’t offer disappearing messages (which I consider important for digital minimalism and cybersecurity.
I noticed this in the article and figured I’d throw my 2 cents in. This might be a spicy take, but I actually can’t stand apps that do this.
When I was in school I had someone harass me online with threats of violence (they spent a couple of hours insulting and threatening me) then lie to the staff that I was harassing them with even more extreme shit. The staff and other students all took their side until I logged in and showed the conversation. If the messages had disappeared I wouldn’t have been able to prove my innocence.
I very firmly want encrypted communications for privacy (I use Signal and Matrix), but I am quite wary of purging communications automatically. That said, it’s anyone’s right to use services that auto delete and my right not to.
I’m curious what other people’s take on this would be.
Deleting messages is still a thing. If there is a message you need to preserve, take a screenshot. If you are worried that someone might think that the screenshot is fake, take a screen recording, or even better, use your phones camera to physically record your screen.
For disappearing messages to work, your conversation partner has to promise they won’t take photos of their screen, and they have to promise to use an app that actually implements the feature instead of just pretending to, and the app developers have to promise to have implemented the code to delete a message when the service says it should
Is there actually a cryptographically-sound and physically-complete method for ensuring that a message is only legible for a temporary duration once it leaves your own device and is delivered to someone elses?
Nope, it is impossible to have messages deleted after a specific time. There is simply no way to do it.
Couldn’t you have blocked them?
I fail to see how that would’ve helped in that situation, it had extended to real life.
That’s why I asked, I need to get his take before I assume anything.
This was almost a decade ago but it was a real life issue extending online, blocking might have made the in person stuff worse. Hard to say, teenagers are awful.
These days I simply don’t keep company I don’t enjoy so it doesn’t become an issue. I also stepped away from posting on social media at all until I recently joined Lemmy and Mastodon.
encrypted email
Besides being a form of messaging (so the text somewhat contradicts itself), typical email is a deeply insecure protocol.
In my opinion, it’s probably impossible to secure without making a new protocol or making such drastic changes that it might as well be considered one.Here are some key concerns regarding the usual PGP-powered encrypted email:
- Email, at a simple level, works much akin to physical email — there’s an “envelope” containing important info regarding the communicating parties, which can’t be encrypted, otherwise the mailing servers wouldn’t know where to forward the messages. This essentially leaks a lot of metadata that can be almost as valuable as the message body itself.
- There’s no forward secrecy — one of the best cryptography features that has become pretty much a commodity in modern systems is forward secrecy, which prevents attackers from decrypting older messages after gaining access to one of the keys.
- While not an issue with the protocol itself, it’s the sad reality and we need to consider — most people use GMail, Outlook and the like, which ultimately need to read your emails in plaintext, for better or worse reasons (search is incredibly useful, but some big players don’t stop there of course :p).
- Another thing is the fact that it’s incredibly easy to have an imbalance of encryption, i.e. someone is encrypting their messages, but others aren’t. With the very popular email culture of quoting (be it top or bottom posting), an unencrypted party in the the conversation can leak important information.
- PGP is… peculiar, so to speak. I has a lot of issues, mostly stemming from its age (which could also be a source of robustness and security, due to being very battle-tested, but I don’t think that’s quite the case with PGP/GPG), tries to do too much and typically has a clunky UI, which impedes wider and proper adoption by less technically people.
This isn’t to say people should definitely stop using and promoting encrypted email, since it can be useful.
It’s just it gives, more often than not, a false sense of security and can lead less proficient users to send sensitive data through this medium which isn’t nearly secure enough for such use cases. Preferably, people with such threat models should opt for better alternatives, most suggested in that article (such as, but definitely not limited to, Signal, SimpleX, Matrix+Olm, XMPP+OTR/OMEMO, sharing files via MagicWormhole, encrypting with tools like age).On a slightly tangential note, I think someone should make a Matrix client with an email client interface. I started working on a new traditional chat client (completely nonfunctional still, very much in-dev), but I’ve been honestly thinking more and more about making one looking like an e-mail client, where there isn’t much focus on instant room-based chats, but rather on longer-lived 1-to-1 and list-like exchange of messages.
I like Signal, but I really miss multi device support. Same issue with Threema.
Yeah that’s a bummer. Signal has multi device support but only for desktop and iPad (yeah, not Android tablets), but you always need to have a master phone device.
It’s been an issue for so long, but this is Signal, they do whatever the f they want.
A workaround to have android has secondary device : https://programming.dev/post/5281504
Ah right, Molly. Have yet to tried it, but looks interesting.
I think I’m too afraid of moving my main stuff to Molly, lest I lose something :P But the UnifiedPush and multiple mobile clients is enticing.
It is not like they couldn’t support it. Simplex Chat has early support and Session has supported it for a long time.
the fact that you like it doesn’t make best or even decent in terms of privacy
But in practical usability
Why do people like Matrix? It’s really slow. Even most of the non-Electron clients consume a ton of resources (even more than Electron apps usually do).
Especially Gomuks, by far the worst offender. It consumes nearly a gigabyte of memory and it’s a TUI.
I think it more comes down to it not being Discord than people liking it.
Well, it’s not privacy-focused… but I do like Revolt for this purpose. It’s performant, looks very similar to Discord, and I think they’re adding E2EE eventually.
deleted by creator
It is centralized and the moderation suck. They banned people for being homophobic because they said they were Christian. You can find more information online.
I attempted to find evidence to support this.
I found one reddit post claiming this, but they themselves did not provide any evidence.
freedom of religion is a human right bruh i did not say anything but i believe in god the banned me and claimed i was being homophobic 1. i said nothing about it 2. stfu even if i was
Not exactly the most compelling piece of evidence, and this was all I could find.
I can’t find it now but there was a person who was banned for saying the were Christian. They didn’t say anything more and the could as well been LGBQ+. There were a few other instances that I am forgetting of bad moderation.
Anyway the centralized nature of Revolt Chat makes it no very appealing for me.
Anyway the centralized nature of Revolt Chat makes it no very appealing for me.
I agree with this. I will probably stick with either matrix or xmpp due, to their federated nature, and strong E2EE. Matrix is a better discord replacement, as it has more features, is more standardized, has a better web client, and has “spaces”, which are somewhat analogous to discord servers.
Xmpp however, is much more lightweight on both servers and clients than matrix, and it’s E2EE works more reliably (none of that "failed to decrypt nonsense), and makes a better E2EE messenger.
It is selfhostable though, so moderation would be an issue of individual servers rather than the whole thing.
The problem is that no one will use your server
The issue has historically been with the server. (It was buggy as hell) These days it is much more stable and less prone to collapse.
I don’t like Matrix because it gives a option to not encrypt communications. Encryption should be enforced and transparent
Also doesn’t force e2ee
Matrix sucks but emojis :3
SimpleX is currently my favourite. Yeah, there are some small concerns, but where aren’t they? I hope SimpleX can grow more popular and I’m also waiting for a full-featured desktop client, so it’ll be easier to convince people to switch.
The missing unifiedpush feature. I don’t need another battery burning messenger.
I hate that simplex is like this.
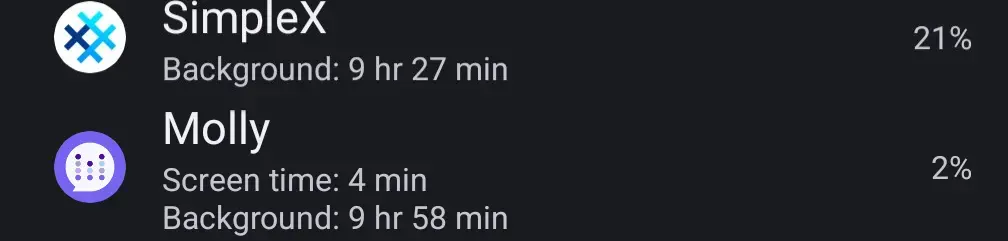
That is my one and only issue with Simplex. It drinks battery lika a Puerto Rican drinks rum on weekends.
There is a full-featured desktop client now! What I am waiting for are third-party lighter clients, because the official one is obscenely heavy.
Oh, I didn’t know it has a flatpak now. That’s cool!
A desktop client that syncs with the mobile client is a must before I can make that switch
I just have a profile on each that are always both in the same groups. IDK about private messaging though.
Simplex=battery eater!
I wish Molly was brought up. It is way better than Signal
In what way? I thought it was just an alternative client for Signal.
It is. It’s just a bit hardened
Only big difference I noticed is it allowed me to log in on 2 phones simultaneously
As a long time user of Session, it is hard to believe someone would describe it as “user-friendly”.
XMPP and Matrix
Matrix is the worst option when it comes to avoiding metadata. A group chat with users on 10 different servers will create ten different places to store the metadata with no way for any user to delete or edit this metadata. Its a privacy nightmare.
How does xmpp handle it?
All decentralized protocols have this issue. The servers need to handle metadata for chat groups, like who is part of which group. If the servers are under individual control, nobody can force them to delete this data. The question is, do you trust a non profit organisation like signal to minimize and delete metadata (which court orders have proven they do) or do you trust all individuals of a group chat to do the same when you manually ask them to.
We’ve been on simplex for a few months, I like it quite a bit. We made diff accounts for each device and added them all to a group.
Notifications arrive reliably on graphene (no google services), and KDE connect.
I don’t love the desktop client and wish I could change text size and scaling. I was able to message the dev about it in simplex and got replies which was cool
Sad that Wire wasn’t mentioned. I think its the only one that encrypts everything, allows anonymous accounts (no phone number needed!), and has independent clients on all platforms (no mobile app install required, but they have one) that seamlessly syncs messages on all clients
Oh, and its free and open-source.
deleted by creator
Yeah, its getting pretty crusty. I think they laid off like 80% of their staff and made a hard fork of the app and never put the new version in f-droid.
They really need to fix that…
Check out Session, built on Lokinet, no signups
It has all the features I mentioned?
Is there a desktop client that doesn’t require you to signup with a mobile app?
Edit: just tried to download it, but I couldn’t find any release signature file. Thats not a good sign.
Yes, but I think the only clients are from Session themselves currently. All platforms, all independent and can have multiple accounts. Everything encrypted by default (and no way to send clear text)
Yeah their signatures and shasums are hosted on github. They’re a small team, which is probably why they rely on it
Here’s their android one at least https://github.com/oxen-io/session-android/releases
I loved it but had to let go because too many times messages didn’t deliver using different devices, different networks, different recipients. This is over years of trying. I really wanted it to work but sadly that was a big reason to stop trying.
Huh, been using it for years and never had that issue. I do have some people complain about notifications, but not lack of delivery
TLDR: Avoid Telegram and WhatsApp. Recommended messengers are Session, Signal, SimpleX and Threema. Honorable mention: Briar.
OK, WhatsApp is owned by Meta and it is proprietary, but why not Telegram?
Effectively does not have end-to-end, phone number required and overall hard to use anonymously, etc.
Doesn’t Signal also require a phone number?
Not anymore if I understand everything correctly
Session should probably be avoided as well, primarily because they’ve disabled things like perfect forward secrecy and a few other security measures that probably should not have been disabled.
Session is dead lmfao
What about Briar? I know its android only but it looks promising for what it can do.
Good for large groups such as a protest
It’s listed as a honorable mention in the article.
Thoughts on using TeleGuard?