
Beehaw
  • Communities
  • Create Post
  • search
    Search
  • Login
  • Sign Up
Ek-Hou-Van-Braai ( Ek-Hou-Van-Braai@piefed.social )  to Programmer Humor@programming.devEnglish · 20 days ago

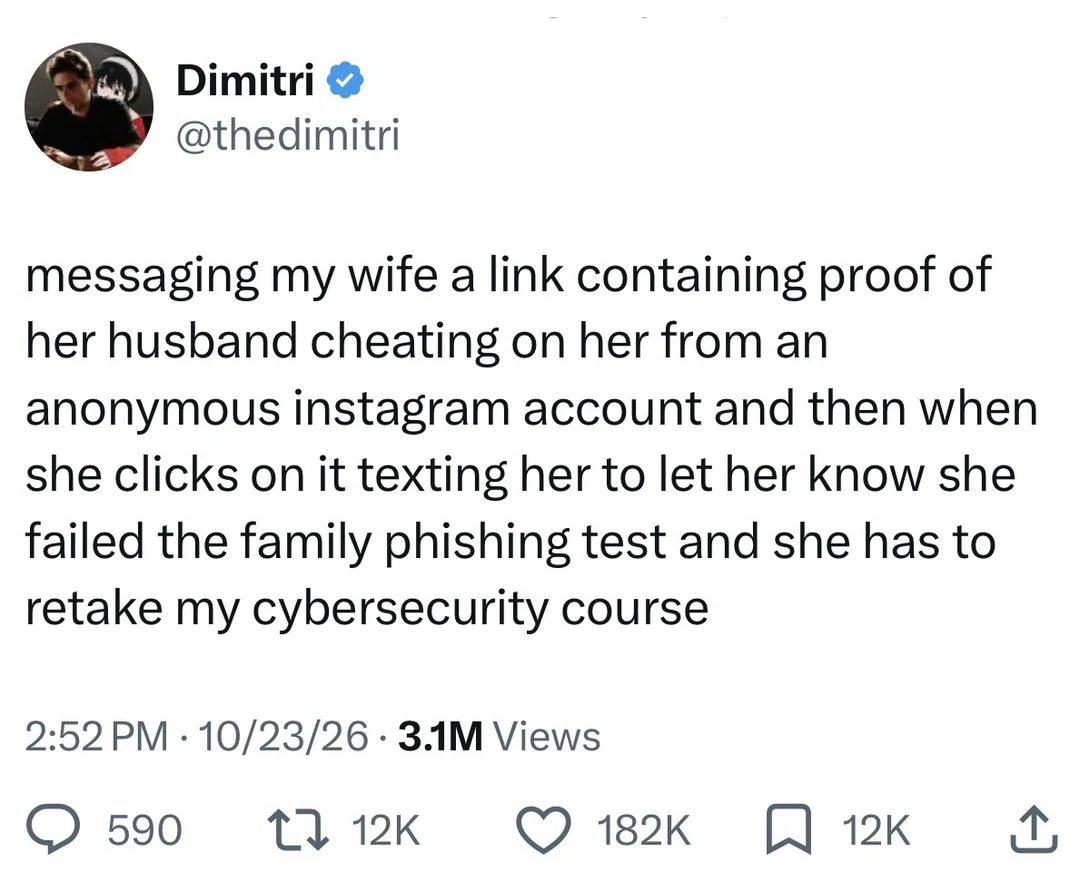
For all the ladies who'd fail this Satan's test

media.piefed.social

message-square
67
link
fedilink
956

For all the ladies who'd fail this Satan's test

media.piefed.social

Ek-Hou-Van-Braai ( Ek-Hou-Van-Braai@piefed.social )  to Programmer Humor@programming.devEnglish · 20 days ago
message-square
67
link
fedilink
alert-triangle
You must log in or register to comment.
  • threeonefour ( threeonefour@piefed.ca ) 
    link
    fedilink
    English
    arrow-up
    158
    ·
    20 days ago

    My current company makes it real easy. All their simulated phishing addresses use the fictitious TLD of “.corn” so I just setup an email rule to filter them.
    • IndignantIguana ( IndignantIguana@piefed.social ) 
      link
      fedilink
      English
      arrow-up
      61
      ·
      edit-2
      20 days ago

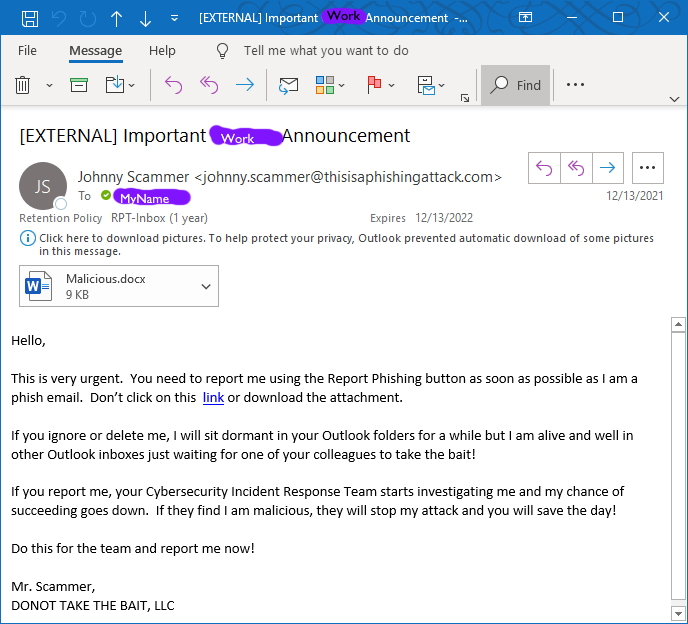
      JBJTAc9nY83cYHV.png

      An actual email sent by my company. (not representative of their usual)

      • korazail ( korazail@eviltoast.org ) 
        link
        fedilink
        English
        arrow-up
        25
        ·
        20 days ago

        That’s pretty cool. Gets the point across - and the reason and results of why it matters to report instead of ignore. Kudos to your team.

      • LiveLM ( LiveLM@lemmy.zip ) 
        link
        fedilink
        English
        arrow-up
        18
        ·
        20 days ago

        Yeah if anyone falls for this lock them out of their computer immediately.

      • Wolf314159 ( Wolf314159@startrek.website ) 
        link
        fedilink
        arrow-up
        12
        ·
        19 days ago

        I delight in reporting genuine emails from my company that look like sophisticated phishing attempts, bonus points if they send a follow-up assuring us that the previous sketchy email was in fact genuine.

      • foodandart ( foodandart@lemmy.zip ) 
        link
        fedilink
        English
        arrow-up
        5
        ·
        20 days ago

        That’s a crack it open with a hex editor, find who sent it, delete then return a note to the sender letting them know you’ve removed the problematic communication, thankyouverymuch… signed ABiggerCuntThanYou@WhyIsMyCompanyWastingMoneyOnThisShit.org

        • wyldrstallyns ( wyldrstallyns@lemmy.dbzer0.com ) 
          link
          fedilink
          English
          arrow-up
          4
          ·
          19 days ago

          That’s how you get assigned to IT overflow tickets, NGL. 😅

          • foodandart ( foodandart@lemmy.zip ) 
            link
            fedilink
            English
            arrow-up
            3
            ·
            18 days ago

            LOL! from the department of Don’t Threaten Me With a Good Time!

            • wyldrstallyns ( wyldrstallyns@lemmy.dbzer0.com ) 
              link
              fedilink
              English
              arrow-up
              3
              ·
              18 days ago

              I’m betting that your current workload and their deadlines would be unaffected, is the rub.

              Don’t get me wrong, I’m right there with ya! Except for the extra work, doubled expectations, and extreme discount to the co. 🙄🤢🤷🏼‍♂️

      • andioop ( andioop@piefed.social ) 
        link
        fedilink
        English
        arrow-up
        1
        ·
        17 days ago

        This is so cute.

    • FaceDeer ( FaceDeer@fedia.io ) 
      link
      fedilink
      arrow-up
      50
      ·
      20 days ago

      A company I was in a few jobs back had several layers of IT department, there was the local studio department that handled our everyday stuff and a “head office” somewhere far away that set policy and handed out budget and whatnot.

      One day “head office” IT decided it was a good idea to send out some fake phishing emails to “test” us. They didn’t tell the local IT department about it, I guess they were also being “tested”. My manager received one and only recognized it as a phishing attempt after he’d clicked just one too many things for it to feel safe to ignore. So he yanked the power on his computer and contacted the local IT department, as is protocol when something potentially dangerous just happened.

      The local network went into lockdown while local IT tried to figure out if something actually dangerous had happened. It cost the studio as a whole several hours of work time, which for a studio our size translated to an obscene dollar cost. Nobody on our side of things did anything wrong, even that one extra “dangerous” click my manager did wasn’t something he could be blamed for - head office had crafted the fake phishing attempt well and his reaction to it would have prevented damage had it been real.

      Head office never tried a stunt like that again.

      • bamboo ( bamboo@lemmy.blahaj.zone ) 
        link
        fedilink
        English
        arrow-up
        8
        ·
        20 days ago

        All I could think as I read this was Dwight’s fire drill from the office

      • AwesomeLowlander ( AwesomeLowlander@sh.itjust.works ) 
        link
        fedilink
        English
        arrow-up
        4
        ·
        20 days ago

        Given how common phishing attempts can be though, shutting down for every single one seems like overkill.

        • FaceDeer ( FaceDeer@fedia.io ) 
          link
          fedilink
          arrow-up
          10
          ·
          20 days ago

          Phishing attempts that got far enough to actually show up in our internal corporate inboxes like that aren’t common, though. They’re normally blocked by the layers of firewalls and whatnot. We almost never saw email on those accounts from outside the organization itself, period.

          And once you’ve run something capable of remote execution on a machine that’s inside the local network, with the sort of privileges that his machine had (he wasn’t just a bureaucratic sort of manager, he was writing code too), you don’t want to mess around.

    • neuracnu ( neuracnu@lemmy.blahaj.zone ) 
      link
      fedilink
      English
      arrow-up
      17
      ·
      20 days ago

      Kemming is 100 level preparedness.

      They need to up their game to cover internationalized homograph vulnerabilities, using roughly similar characters from different international alphabets to create totally different domain names:

      example.com
      exаmple.com

      They look identical but are entirely different.

      https://en.wikipedia.org/wiki/IDN_homograph_attack

      • skulblaka ( skulblaka@sh.itjust.works ) 
        link
        fedilink
        arrow-up
        8
        ·
        20 days ago

        Well that’s just rude

      • Jack ( Jack@lemmy.ca ) 
        link
        fedilink
        English
        arrow-up
        2
        ·
        20 days ago

        They look identical but are entirely different.

        They "a"s don’t look identical at all with a good font like Atkinson Hyperlegible Next, which also very clearly differentiates between

        • 0 and O
        • I and l

        etc…

    • hemko ( hemko@lemmy.dbzer0.com ) 
      link
      fedilink
      English
      arrow-up
      11
      ·
      20 days ago

      My company is using phishing simulations from a company that puts their company name in the x headers or every email, so that’s also easy filter.

      As a bonus, that filter also throws all the full security training courses to junk

    • LastYearsIrritant ( LastYearsIrritant@sopuli.xyz ) 
      link
      fedilink
      English
      arrow-up
      9
      ·
      20 days ago

      If your company contracts with phish.me then that URL is actually in the email header metadata.

      Just set up a rule for the word phish to a special folder, and then you can use the “report” button on everything in that folder to get the credit.

      • Honytawk ( Honytawk@discuss.tchncs.de ) 
        link
        fedilink
        English
        arrow-up
        2
        ·
        20 days ago

        So what do you do when you get an actual phishing mail that doesn’t use that word?

        • LastYearsIrritant ( LastYearsIrritant@sopuli.xyz ) 
          link
          fedilink
          English
          arrow-up
          2
          ·
          19 days ago

    • ivan ( ivan@piefed.social ) 
      link
      fedilink
      English
      arrow-up
      8
      ·
      20 days ago

      My place has this thing where most phishing test emails are obvious but every once in a while they’ll drop a really good one, sometimes these even pose as our managers.

      • gjoel ( gjoel@programming.dev ) 
        link
        fedilink
        arrow-up
        3
        ·
        20 days ago

        The company I work for has lots of training to recognize phishing attempts, and then they proceed to send emails that tick most of the “avoid this” boxes.

    • hypnicjerk ( hypnicjerk@piefed.social ) 
      link
      fedilink
      English
      arrow-up
      8
      ·
      20 days ago

      lucky you. they fail us if we don’t right click report phishing.

      • addie ( addie@feddit.uk ) 
        link
        fedilink
        arrow-up
        6
        ·
        20 days ago

        Can still set up a header-matching rule - just need to mark the email with a label, so you can report it without even having to read it.

    • socsa ( socsa@piefed.social ) 
      link
      fedilink
      English
      arrow-up
      7
      ·
      20 days ago

      I just take it one step farther and never open any email. If it’s important you will CC my manager and he will physically come by my office and tell me about the email, giving me multi-factor phishing protection. If he demands I open an email then I am absolved of responsibility.

      • decayedproton ( decayedproton@beehaw.org ) 
        link
        fedilink
        arrow-up
        1
        ·
        20 days ago

        If he demands I open an email then I am absolved of responsibility.

        You’d expect it to work that way. But in the real world, not always.

    • Catoblepas ( Catoblepas@lemmy.blahaj.zone ) 
      link
      fedilink
      arrow-up
      3
      ·
      20 days ago

      Lmfao, .corn sounds like an instance someone would spin up to compete with lemmy.beans

    • Captain Aggravated ( captain_aggravated@sh.itjust.works ) 
      link
      fedilink
      English
      arrow-up
      2
      ·
      19 days ago

      Oh man y’all remember the actual phishing campaign of messages from customer-service@bankofarnerica. com?

    • Honytawk ( Honytawk@discuss.tchncs.de ) 
      link
      fedilink
      English
      arrow-up
      1
      ·
      20 days ago

      So what do you do when you get an actual phishing mail that doesn’t use that TLD?

      • Laurel Raven ( laurelraven@lemmy.zip ) 
        link
        fedilink
        English
        arrow-up
        2
        ·
        19 days ago

        The phake phish company isn’t monitoring those, so no worries!

  • Trigger2_2000 ( Trigger2_2000@sh.itjust.works ) 
    link
    fedilink
    arrow-up
    40
    ·
    20 days ago

    Just read this to a beautiful woman I know.

    Her response: That’s not going to end near as well/funny as you think/hope it will.

    • minorkeys ( minorkeys@sh.itjust.works ) 
      link
      fedilink
      arrow-up
      39
      ·
      20 days ago

      Neither is your future if your wife maintains such easily exploited vulnerabilities.

    • andioop ( andioop@piefed.social ) 
      link
      fedilink
      English
      arrow-up
      2
      ·
      edit-2
      17 days ago

      I like to think I’d find this hilarious if done to me. I found it funny enough to save and send to my friends. On the other hand, I’m reading it as a joke now online, not actually going through it, and I can see how if it had been done to me I might be upset. Not sure if I would have been or not!

      (Am woman in a hetero relationship.)

      • Trigger2_2000 ( Trigger2_2000@sh.itjust.works ) 
        link
        fedilink
        arrow-up
        2
        ·
        17 days ago

        Beautiful (hetro) woman I talk to says: She would find it funny (her husband is a big joker), but yes, it could be stressful at the onset to be told your husband is cheating on you.

  • SparroHawc ( SparroHawc@piefed.world ) 
    link
    fedilink
    English
    arrow-up
    38
    ·
    20 days ago

    I failed one of those because I have script blockers on my browser and I wanted to see what the scam was.

    • MummifiedClient5000 ( MummifiedClient5000@feddit.dk ) 
      link
      fedilink
      English
      arrow-up
      21
      ·
      20 days ago

      The URL is likely unique to identify you as soon as you have clicked.

      • SparroHawc ( SparroHawc@piefed.world ) 
        link
        fedilink
        English
        arrow-up
        7
        ·
        20 days ago

        Yeah, that’s why I had to take the online safety course again.

        It wouldn’t have been able to do much to my computer though, if it really was a suspicious site.

        • pinball_wizard ( pinball_wizard@lemmy.zip ) 
          link
          fedilink
          arrow-up
          5
          ·
          20 days ago

          I got to take security training for that once, too.

          It was worth it.

      • explodicle ( explodicle@sh.itjust.works ) 
        link
        fedilink
        English
        arrow-up
        4
        ·
        20 days ago

        Simply write a script to cycle through thousands of URLs. The whole company will get identified and then nobody has to retake the training.

        • MummifiedClient5000 ( MummifiedClient5000@feddit.dk ) 
          link
          fedilink
          English
          arrow-up
          5
          ·
          20 days ago

          I suspect that there are more than a few thousands URLs to if you want to go down that route.

    • Ekky ( ekky@sopuli.xyz ) 
      link
      fedilink
      English
      arrow-up
      17
      ·
      20 days ago

      Same, script blocker, virtual machine, etc. Found that apparently you are not meant to forward/report the scam to IT either.

      Moral of story: Never inform the company of any suspicious behavior; just ignore it.

      • Ek-Hou-Van-Braai ( Ek-Hou-Van-Braai@piefed.social ) OP
        link
        fedilink
        English
        arrow-up
        12
        ·
        20 days ago

        There’s a button that says report phishing for many companies

        • baguettefish ( baguettefish@discuss.tchncs.de ) 
          link
          fedilink
          English
          arrow-up
          13
          ·
          20 days ago

          some phishing emails also have a button like that, very funny

        • Ekky ( ekky@sopuli.xyz ) 
          link
          fedilink
          English
          arrow-up
          5
          ·
          20 days ago

          Keyword here being “many companies”.

        • andioop ( andioop@piefed.social ) 
          link
          fedilink
          English
          arrow-up
          1
          ·
          8 days ago

          deleted by creator

  • SpaceCowboy ( SpaceCowboy@lemmy.ca ) 
    link
    fedilink
    arrow-up
    32
    ·
    20 days ago

    Sounds kinda like the Tale of Foolish Curiosity from Don Quixote. Spoiler: the wife was a good woman and wouldn’t have cheated on the guy… until he started being an asshole by subjecting her to endless tests to prove her virtue.

  • Malica ( Malica@lemmy.zip ) 
    link
    fedilink
    arrow-up
    26
    ·
    20 days ago

    I saw one with a bunch of maga triggers. The Democrats are doing what!? 😱 they click every time.

    • hessenjunge ( hessenjunge@discuss.tchncs.de ) 
      link
      fedilink
      arrow-up
      13
      ·
      20 days ago

      May their PCs be infected and their accounts be emptied.

  • SavvyWolf ( savvywolf@pawb.social ) 
    link
    fedilink
    English
    arrow-up
    23
    ·
    20 days ago

    Note that at no point does he claim this “proof” is falsified.

  • Mika ( Mika@piefed.ca ) 
    link
    fedilink
    English
    arrow-up
    18
    ·
    20 days ago

    Just don’t read the mails and you won’t get fished

  • Honytawk ( Honytawk@discuss.tchncs.de ) 
    link
    fedilink
    English
    arrow-up
    10
    ·
    20 days ago

    All these people setting up filters don’t understand it is supposed to train you in case a real phishing attempt is made.

    Those filters aren’t going to stop real ones.

    But if you want to blow up the database server you need to work on because you couldn’t be bothered to click a button when a phishing test comes around, then you better quit your job in tech.

    I swear, developers are some of the biggest security concerns in any company. They complain the moment some access is blocked for good reason. Much bigger concern than old nancy “never-had-a-computer-at-home” clicks-a-lot.

    • Wolf314159 ( Wolf314159@startrek.website ) 
      link
      fedilink
      arrow-up
      8
      ·
      19 days ago

      If the fake phishing emails can be caught by my very rudimentary filter they weren’t particularly good anyway. Besides, I still have to look at those emails and report them, otherwise my IT still counts it as a strike against me. Win-win. IT continues to keep me on my toes and I don’t have to take another 30min training course because I ignored an email for a day or two.

  • Geobloke ( Geobloke@aussie.zone ) 
    link
    fedilink
    arrow-up
    9
    ·
    20 days ago

    This kills the trust

    • Saapas ( Saapas@piefed.zip ) 
      link
      fedilink
      English
      arrow-up
      8
      ·
      20 days ago

      Yeah, the wife didn’t trust the husband and clicked the link. Shameful, tbh

  • Miisha ♀️ ( QueenMiisha@lemmy.blahaj.zone ) 
    link
    fedilink
    English
    arrow-up
    9
    ·
    20 days ago

    I’d fail this so freaking hard omfg 😭

    Bf sends link? I click
    Complete internet stranger sends link? I click
    Thoughts? None
    Brain? Empty
    Other family members send me a link? Eeh, I get a bit suspicious, then I click 😂

    God I’m so old…at twenty already 😭

    • Teagan ( IntroSkeptic@lemmy.blahaj.zone ) 
      link
      fedilink
      arrow-up
      6
      ·
      20 days ago

      IM 23 MIISH 😭

    • ThotDragon ( thoughtfuldragon@lemmy.blahaj.zone ) 
      link
      fedilink
      English
      arrow-up
      5
      ·
      20 days ago

      You have to get old when you’re young that way you’ve got experience.

    • Vetis ( Vetis@sh.itjust.works ) 
      link
      fedilink
      arrow-up
      4
      ·
      20 days ago

      Damn, you are doomed and you know it eh

      • Miisha ♀️ ( QueenMiisha@lemmy.blahaj.zone ) 
        link
        fedilink
        English
        arrow-up
        1
        ·
        19 days ago

        I know, I know okay? 😭

        There are people that are not very experienced with using modern computers…and then there are people like me, who willingly choose stupidity.

        I honestly am doomed 😭

    • psycholocomotor_no2 ( psycholocomotor_no2@lemmy.blahaj.zone ) 
      link
      fedilink
      arrow-up
      4
      ·
      20 days ago

      https://ferociter.itch.io/cataractae here’s a random link for y’all.

      • Miisha ♀️ ( QueenMiisha@lemmy.blahaj.zone ) 
        link
        fedilink
        English
        arrow-up
        1
        ·
        19 days ago

        Omg omg shiny link :3

        Oh…actually looks like a really fun game. And pretty too.

        I think I’ll give it a try. Thanks 💜

  • wyldrstallyns ( wyldrstallyns@lemmy.dbzer0.com ) 
    link
    fedilink
    English
    arrow-up
    7
    ·
    19 days ago

    It’s a honey pot of a different color! Genius!

  • bedwyr ( bedwyr@piefed.ca ) 
    link
    fedilink
    English
    arrow-up
    6
    ·
    20 days ago

    So what about links on social media, say you beefed with the tankies, then one on an alt account sends you a link to an article, could be phishing no? What to do then?

    • MonkeMischief ( MonkeMischief@lemmy.today ) 
      link
      fedilink
      arrow-up
      28
      ·
      edit-2
      20 days ago

      Take a while to open it. If they Ping you and keep asking “Why haven’t you clicked the link yet?!” You’ll know they were Putin a trap in your DMs, and you got them by Stalin.

      That Marx them as a phisher, Lenin credence to the simple fact that you can’t trust anybody on the internet these days.

      Can’t be too careful! They come at you from so many Engels.

      😎<br> 👉👉

  • truxnell ( truxnell@quokk.au ) 
    link
    fedilink
    English
    arrow-up
    4
    ·
    20 days ago

    Second panel: this is the setup to his torrid public affairs, which he now has deniability for

  • ScoffingLizard ( ScoffingLizard@lemmy.dbzer0.com ) 
    link
    fedilink
    arrow-up
    1
    ·
    19 days ago

    I gotta do this.

  • sleepthief ( sleepthief@piefed.social ) 
    link
    fedilink
    English
    arrow-up
    1
    ·
    14 days ago

    Chaotic lawful 😂

Programmer Humor@programming.dev

programmer_humor@programming.dev

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !programmer_humor@programming.dev

Welcome to Programmer Humor!

This is a place where you can post jokes, memes, humor, etc. related to programming!

For sharing awful code theres also Programming Horror.

Rules

  • Keep content in english
  • No advertisements
  • Posts must be related to programming or programmer topics
    • If the mod doesn’t find it funny, you’re banned. Ha-ha!.. For real: do not use the community for “statements”. There are other places for such content. Keep it chill and funny.
Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 231 users / day
  • 2.63K users / week
  • 5.11K users / month
  • 8.39K users / 6 months
  • 465 local subscribers
  • 34.2K subscribers
  • 1.66K Posts
  • 27.5K Comments
  • Modlog
  • mods:
  • Feyter ( Feyter@programming.dev ) 
  • adr1an ( anzo@programming.dev ) 
  • BurningTurtle ( BurningTurtle@programming.dev ) 
  • Pierre-Yves Lapersonne ( pylapp@programming.dev ) 
  • BE: 0.19.21
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code